






PCI DSS Certification in Cebu
Picture a card swipe at a Mactan resort, an online order from a Cebu web store or a phone payment taken in Lahug. Each one carries the same expectation. The card data must be handled to the Payment Card Industry Data Security Standard. PCI DSS certification in Cebu is how local merchants and service providers prove this to their acquiring bank, the card brands and their clients.
Univate Global prepares Cebu organizations for PCI DSS v4.0.1 validation. We map where card data flows, shrink the cardholder data environment where we can, close the control gaps and get your evidence ready. When the formal assessment arrives, whether a Qualified Security Assessor review or a Self-Assessment Questionnaire, your team is ready for it.
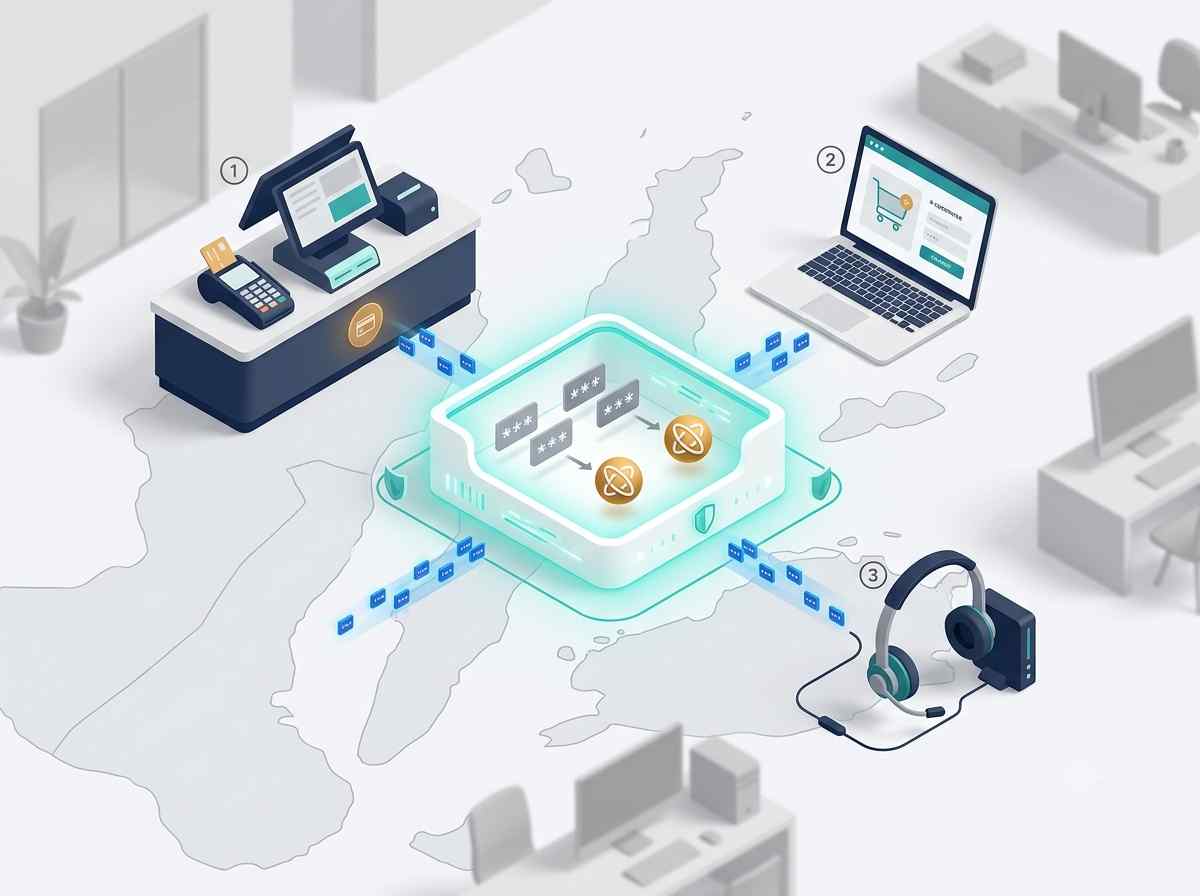
Our consultants work around your payment setup rather than a generic checklist. A resort with point-of-sale terminals in its restaurants needs a different plan from a fintech running its own payment API. A BPO taking card details over the phone needs a different plan again. We tailor the work to the way money actually moves through your business.
Free ConsultationContact Us
Our Clients
PCI DSS Certification in Cebu for BPOs, Resorts and Payment Providers
PCI DSS applies to any organization that stores, processes or transmits cardholder data. It also applies to organizations whose systems could affect the security of that data. In Metro Cebu, the demand comes from a wide mix of businesses.
Contact centers and IT-BPM operators are near the top of the list. Many Cebu BPOs take card payments, process refunds or handle billing disputes for US, UK and Australian brands. Their clients usually write PCI DSS obligations straight into the service agreement and ask for an Attestation of Compliance before go-live.
Hotels, beach resorts and travel businesses are another large group. Properties on Mactan Island and along the Lapu-Lapu coastline take cards at reception, restaurants, spas and booking engines. Tour operators, dive shops and travel agencies serving visitors arriving through Mactan-Cebu International Airport face the same requirements from their acquiring banks.
Fintech firms, payment service providers and e-commerce companies have the most technical scope. Payment gateways, digital wallets, marketplaces and web stores must all show how card data is protected. Alternatively, they must show it never enters their systems.
Retailers and mall-based chains, private hospitals and schools that collect tuition by card complete the picture. Even an organization that only takes a few hundred card payments a year has a validation duty. The method is simply lighter.
How PCI DSS Certification Works in Cebu
The Payment Card Industry Data Security Standard is maintained by the PCI Security Standards Council, which was founded by the major card brands. The current version is PCI DSS v4.0.1, published in June 2024. The requirements that v4.0 had marked as future-dated became mandatory on 31 March 2025. Any assessment you face now is measured against the full set.
One point is worth stating plainly. PCI DSS is technically a compliance validation, not a certificate issued by a certification body. “Certification” is simply the term most people search for and use. What you receive is a validated status. It is documented in a Report on Compliance (ROC) or a Self-Assessment Questionnaire (SAQ), then summarized in an Attestation of Compliance (AOC).
Which route you follow depends on your level. The card brands define merchant levels and service provider levels, largely by annual transaction volume. Your acquiring bank then tells you how you must validate. Higher-volume organizations need an on-site assessment by a Qualified Security Assessor (QSA), who writes the ROC. Smaller merchants usually complete the SAQ that matches how they accept cards.
Univate is not a QSA. Our role is to prepare your organization, fix the gaps and then work alongside the QSA or your internal SAQ signatory during validation. Keeping the roles separate protects the independence of the assessment your bank relies on.
Why Cebu Businesses Invest in PCI DSS Certification
For many Cebu companies, the push comes from outside. An acquiring bank sends a compliance letter. A US retailer outsourcing its customer service asks for an AOC in its request for proposal. A booking platform partner refuses to integrate until your web checkout is validated. In each case, PCI DSS certification in Cebu becomes a condition of doing business rather than a nice-to-have.
There is also a direct financial reason. A card data breach can bring forensic investigation costs, card replacement charges and higher processing fees. Your bank may also withdraw your ability to accept cards. For a resort in peak season or an online store during a sale, that interruption would be severe.
PCI DSS, the Data Privacy Act and BSP Rules
Cardholder names and card numbers are personal information under the Data Privacy Act of 2012 (Republic Act 10173). That means the National Privacy Commission expects reasonable security measures around them, and a breach may need to be reported. Banks, e-money issuers and other institutions supervised by the Bangko Sentral ng Pilipinas (BSP) must also follow BSP rules on IT risk management. PCI DSS does not replace either regime. However, its detailed controls give you concrete, testable evidence for much of the security side of both.
PCI DSS Requirements: What Your Organization Will Need
PCI DSS v4.0.1 sets out 12 principal requirements grouped under six goals. The goals are a secure network and systems, protected account data, vulnerability management, strong access control, regular monitoring and testing, and an information security policy. Every PCI DSS certification in Cebu that we support works through these 12 requirements:
- Requirement 1: Install and maintain network security controls
- Requirement 2: Apply secure configurations to all system components
- Requirement 3: Protect stored account data
- Requirement 4: Protect cardholder data with strong cryptography during transmission over open, public networks
- Requirement 5: Protect all systems and networks from malicious software
- Requirement 6: Develop and maintain secure systems and software
- Requirement 7: Restrict access to system components and cardholder data by business need to know
- Requirement 8: Identify users and authenticate access to system components
- Requirement 9: Restrict physical access to cardholder data
- Requirement 10: Log and monitor all access to system components and cardholder data
- Requirement 11: Test security of systems and networks regularly
- Requirement 12: Support information security with organizational policies and programs
How many of these apply in full depends on your scope. A merchant that sends every payment to a hosted payment page may answer a short SAQ. A service provider storing card data in its own databases faces hundreds of detailed sub-requirements. That is why scoping the cardholder data environment (CDE) comes first, before any policy is written.
Assessors also want proof over time, not just on the day. Quarterly external scans, log reviews, access reviews and training records all need to exist across the year. We help you set up the routines that generate this evidence naturally, so validation does not turn into a last-minute scramble.
Our Process for PCI DSS Certification in Cebu
We run each engagement in six stages. Every stage has a defined output, so your finance, IT and operations teams always know what has been done and what is still open.
Step 1 – Card Data Discovery and CDE Scoping
We trace every path card data takes through your business. That includes card terminals, phone payments, web checkouts, booking engines, call recordings, spreadsheets and third-party processors. The result is a data flow diagram and a defined CDE. We also confirm your merchant or service provider level with your acquiring bank, which decides whether a ROC or an SAQ applies.
Step 2 – Gap Assessment Against PCI DSS v4.0.1
With the scope agreed, we compare your current controls against each applicable requirement. You receive a prioritized gap register that separates quick fixes from larger projects. Where the gaps are expensive, we look for ways to shrink scope instead, such as network segmentation, tokenization or point-to-point encryption (P2PE).
Step 3 – Remediation and Documentation
Your teams then close the gaps with our guidance. Typical work includes firewall rule reviews, hardened configuration standards, multi-factor authentication and centralized logging. It may also cover secure coding and the targeted risk analyses that v4.0.1 calls for. We draft the policies and procedures the standard expects and align them with how your people actually work.
Step 4 – Readiness Review, ASV Scans and Penetration Testing
Before the formal assessment, we run a full readiness review that mirrors how a QSA will test you. Your organization arranges quarterly external scans through an Approved Scanning Vendor (ASV). You also complete the annual penetration test, with segmentation testing where segmentation reduces scope. We help you track findings through to clean, passing results.
Step 5 – QSA Assessment or Self-Assessment Questionnaire
Where a ROC is needed, a QSA company carries out the assessment and issues the ROC and AOC. We stay alongside your team to explain evidence, answer follow-up requests and handle remediation of any findings. For SAQ merchants, we help you choose the correct SAQ type, complete it accurately and prepare the AOC for your bank.
Step 6 – Annual Revalidation and Continuous Compliance
Validation is not a one-time event. PCI DSS must be revalidated every year, and quarterly ASV scans must keep passing in between. We can support your team with a compliance calendar, periodic control checks, change reviews and preparation for the next annual cycle. Your controls then stay effective all year, not just during assessment month.
Typical PCI DSS Timeline for Cebu Organizations
The table below gives indicative durations for a single-site merchant or service provider with a moderate CDE. Larger scopes, custom payment software or heavy remediation will extend these periods.
| Phase | Key activities | Indicative duration | Main output |
|---|---|---|---|
| Discovery and scoping | Map card data flows, define the CDE, confirm level with the acquiring bank | 1–2 weeks | Data flow diagram and scope statement |
| Gap assessment | Test controls against applicable v4.0.1 requirements | 2–3 weeks | Prioritized gap register |
| Remediation | Segmentation, hardening, MFA, logging, policies and training | 6–16 weeks | Remediated controls and documentation |
| Readiness review | Mock assessment, ASV scans, penetration and segmentation testing | 2–4 weeks | Readiness report and passing scan results |
| Validation | QSA assessment or completed SAQ | 2–6 weeks, including scheduling | ROC or SAQ, plus a signed AOC |
Most Cebu merchants on an SAQ route finish in two to four months. Service providers and Level 1 merchants facing a full QSA assessment often need four to nine months. Remediation and the evidence periods the assessor expects drive most of that time.
PCI DSS Certification in Cebu: Cost and Timeline
No honest consultant can quote a PCI DSS project before seeing how cards move through your business. A small boutique hotel and a payment gateway are not comparable engagements. These are the factors that drive the cost of PCI DSS certification in Cebu.
Scope and Size of the Cardholder Data Environment
The more systems, people and locations that touch card data, the more there is to secure and test. A flat network where card data can reach every workstation puts everything in scope. A tightly defined CDE keeps effort, and cost, contained.
Merchant or Service Provider Level
Your level decides whether you complete an SAQ or need a full QSA assessment with a ROC. Service providers, such as BPOs and payment processors handling card data for clients, generally face more requirements than merchants of similar size.
Segmentation and Remediation Effort
Investing in network segmentation, tokenization or P2PE terminals can remove large parts of your environment from scope. Organizations with older point-of-sale systems, shared admin accounts or no central logging will spend more on remediation before validation.
QSA, ASV and Consulting Fees
Your total investment has several separate parts. Consulting support covers scoping, gap assessment and remediation guidance. The QSA’s fee covers the assessment and ROC where one is required. ASV fees cover the quarterly external scans, and penetration testing is usually a separate engagement.
QSAs and ASVs are qualified and listed by the PCI Security Standards Council. Banks and card brands only accept results from assessors and scanning vendors in good standing. Check the Council’s listings before you sign. Once we understand your scope, we give you a clear, itemized quote for our part of the work.
On timing, the biggest variable is usually remediation. A team that can quickly re-architect its network or move to hosted payment pages will reach validation much sooner. For national context and multi-city scopes, see our PCI DSS certification in the Philippines page.
Benefits of PCI DSS Certification for Cebu Businesses
The returns from PCI DSS certification in Cebu reach beyond keeping your acquiring bank satisfied. Done well, the program improves how your organization handles risk, sales and technology.
Uninterrupted Card Acceptance
Validated compliance keeps your merchant account in good standing. For resorts, retailers and online sellers, the ability to take cards without interruption is often the difference between a strong season and a lost one.
More Outsourcing and Partnership Deals
Overseas brands choosing a Cebu contact center for billing or collections work want to see a current AOC. Payment platforms and travel booking partners ask for the same before integration. Validation removes a common blocker from the sales cycle.
Lower Exposure to Card Fraud and Breaches
The standard targets the weaknesses attackers exploit most, from unpatched systems and weak passwords to skimming devices and insecure web checkouts. Closing these reduces the chance of a breach and the costs that follow one.
A Smaller, Simpler Environment
Scoping and segmentation often reveal card data stored in places nobody remembered, such as old spreadsheets, email inboxes and call recordings. Removing it shrinks your risk and makes every future assessment cheaper.
A Platform for Broader Security Programs
Many PCI DSS controls overlap with ISO 27001 and privacy frameworks. Once your PCI program is running, extending it toward ISO 27001 certification in Cebu or ISO 27701 privacy management takes far less effort.
Why Cebu Companies Choose Univate for PCI DSS
Univate has consulted more than 300 enterprises on cybersecurity and compliance. Our team has delivered over 1,000 audit man-days across critical infrastructure and regulated industries. We have also led more than 500 executive sessions on cybersecurity, AI governance and data privacy. Our consultants include CISA-certified professionals and specialists with decades of experience in security, risk and governance. That depth shapes how we approach PCI DSS certification in Cebu, with a focus on scope reduction and evidence that survives scrutiny.
We are a consultant, not a QSA, and we say so from the first meeting. That independence means our advice is aimed at getting you compliant at the lowest sensible scope. It is never aimed at enlarging an assessment. We coordinate closely with your chosen QSA and ASV, so their requests reach a prepared team. Our Philippine office in Makati supports Cebu engagements with remote workshops and on-site visits at key milestones.
Many Cebu organizations also need SOC 2 reports for US clients or a continuity plan for typhoon season. We design your PCI controls so they can be reused for SOC 2 and ISO 22301 business continuity.
PCI DSS Certification Services Across Cebu
We deliver PCI DSS certification in Cebu through a hybrid model. Data flow workshops, document reviews and progress calls run remotely. Site visits are planned for card data discovery, physical security checks of terminals and server rooms, and readiness reviews.
In Cebu City, we work with contact centers and software firms in Cebu IT Park in Lahug and Cebu Business Park. We also support retail and hospitality operators around the South Road Properties and merchants in the downtown Colon area. In Mandaue, we support retailers, distributors and online sellers along A.S. Fortuna and the North Reclamation Area. On Mactan Island, we support resorts, hotels, travel operators and airport-linked businesses across Lapu-Lapu City, as well as companies in the Mactan Economic Zone.
We also support hospitals, schools and growing merchants in Talisay, Consolacion, Liloan and Minglanilla. The same applies to organizations in Bohol and Negros Oriental that take card payments from visitors. Many of these clients pair PCI work with quality programs such as ISO 9001 certification in Cebu.
Planning PCI DSS certification in Cebu?
Tell us about your scope, your sites and your timeline, and we will come back with a clear plan.
Client Testimonials
It was really a great partnership with their team.
Sultan
I had the pleasure and opportunity of working with Univate Solutions on a couple of High Maturity (ML5) CMMI appraisals and found them to be one of the best.
Amulya P
Team Univate holds many professional approaches.
Ashish Sherlekar
PCI DSS Certification in Cebu: Frequently Asked Questions
How long does PCI DSS certification in Cebu take?
Merchants validating through an SAQ typically finish in two to four months. Service providers and higher-level merchants needing a QSA assessment usually take four to nine months. Remediation effort and the size of your CDE are the main factors.
Do we need a QSA, or can we complete a Self-Assessment Questionnaire?
It depends on your merchant or service provider level and on what your acquiring bank requires. Higher-volume organizations generally need a QSA to produce a Report on Compliance. Smaller merchants usually complete the SAQ that fits their payment channels.
Is PCI DSS required by Philippine law?
PCI DSS is a contractual standard enforced through the card brands and acquiring banks, not a Philippine statute. In practice, you cannot keep accepting cards without it. It also supports your security obligations under the Data Privacy Act and, for supervised institutions, BSP rules.
Our resort uses a third-party payment gateway. Are we still in scope?
Usually, yes, but your scope may be much smaller. Outsourcing payment processing reduces your obligations without removing them entirely. Your terminals, staff procedures and the pages that redirect guests to the gateway can still be in scope.
What is an ASV scan, and how often do we need one?
An ASV scan is an external vulnerability scan of your internet-facing systems by an Approved Scanning Vendor. It is required every quarter for in-scope systems, and failing results must be fixed and rescanned until they pass.
Can Univate carry out our PCI DSS assessment?
No. Univate is a consultant, not a QSA, so we do not issue a ROC or sign your AOC. We prepare your organization, close the gaps and work alongside your chosen QSA, or support you while you complete the SAQ.
What changed with PCI DSS v4.0.1?
Version 4.0.1, published in June 2024, is a limited revision of v4.0 that clarifies wording and guidance. The bigger change is that the future-dated v4.0 requirements became mandatory on 31 March 2025. Examples include broader multi-factor authentication and protection of web payment pages.
How often does PCI DSS validation need to be renewed?
Validation is annual. Each year you complete a new ROC or SAQ and AOC, supported by four quarters of passing ASV scans and an up-to-date penetration test.
Can a Cebu IT Park contact center reduce its PCI scope?
Yes. Common approaches include pause-and-resume call recording, payment IVR or DTMF masking so agents never hear card numbers, and segmented networks for payment work. Done properly, these can take most of the agent floor out of scope.
Start Your PCI DSS Certification Project in Cebu
Perhaps your acquiring bank has set a deadline, or a client has asked for your AOC. Either way, the first step is a short conversation about how you take payments today. Our consultants will review your setup, outline the likely scope and validation route, and send an itemized proposal for PCI DSS certification in Cebu.
Book a Free Consultation Call +63 963 451 6528Prefer to talk first? Call our Philippines team on +63 963 451 6528, or send us your requirements through the contact form.
Email: info@univateglobal.com






