






CSA STAR Certification in Manila
Cloud buyers no longer accept a vague promise that their data is “secure in the cloud.” They want to see exactly which controls a provider runs and who checked them. CSA STAR certification in Manila gives cloud, SaaS and managed service providers a public, structured way to show that. It is built on the Cloud Security Alliance’s own control framework and is recognized by enterprise buyers worldwide.
Univate Global prepares Manila organizations for the Cloud Security Alliance’s Security, Trust, Assurance and Risk (STAR) program. We help you choose the right level and map your controls to the Cloud Controls Matrix. We then complete the questionnaire with you and prepare for a third-party audit when needed. We also plan your move to the newest version of the matrix.
Your platform might run from a server room in Santa Mesa or a hosted environment managed from Ortigas Center. It might be a public cloud tenant run from an office in Ermita. In each case, the questions are the same. Which security duties sit with you, which sit with your cloud provider, and can you prove both? We build your STAR evidence around those answers.
Free ConsultationContact Us
Our Clients
CSA STAR Certification in Manila for SaaS Providers, Data Centers and Financial Services
CSA STAR is designed for organizations that deliver services from the cloud, not for every business that simply uses cloud tools. In the capital and the wider metro, three groups make up most of the demand.
SaaS companies and software firms are the largest group. Think of a Manila team building a payroll platform, a learning system for Sampaloc universities or a tracking app for Port Area importers. Each sells to enterprises that send long vendor questionnaires. A published STAR entry answers many of those questions before they are asked.
Data center operators, hosting firms and managed service providers form the second group. Their customers want to know how physical security, virtualization, encryption keys and backups are handled. Because these providers sit underneath other companies’ cloud services, their own STAR posture often becomes part of their customers’ evidence.
Banks, fintech companies and the service providers behind them are the third group. Financial institutions supervised by the Bangko Sentral ng Pilipinas are moving workloads to the cloud, and they need assurance from every outsourced provider. A fintech offering a payments or lending platform to Manila banks may be asked for STAR alongside other security reports.
BPOs that run cloud-based contact center or analytics platforms, government contractors hosting citizen services, and hospital IT teams serving groups in Ermita and Malate are also showing interest. Size is not the deciding factor. A ten-person SaaS start-up with enterprise clients can benefit as much as a large provider.
How CSA STAR Certification Works in Manila
The Cloud Security Alliance (CSA) is a nonprofit that publishes security guidance for cloud computing. Its STAR program rests on two documents. The Cloud Controls Matrix (CCM) is a set of cloud-specific security controls organized into 17 domains. The Consensus Assessments Initiative Questionnaire (CAIQ) turns those controls into yes-or-no questions with space for explanation.
CSA released CCM v4.1 on 28 January 2026. It added 11 new control specifications and removed one identity and access management control. The matching CAIQ v4.1 contains 283 questions. STAR Registry submissions based on CCM v4 are still accepted until December 2027. After that, only v4.1 submissions will be accepted, so new projects should generally start on v4.1.
The program has two main levels, and only one route actually produces a certificate. That surprises many people, so it is worth saying clearly. Level 1 is a self-assessment. You complete the CAIQ and publish it on the public STAR Registry, with no independent auditor involved.
Level 2 adds third-party assurance, and it comes in two forms. STAR Certification combines ISO/IEC 27001 certification with the CCM and is audited by a CSA-approved certification body. Your ISO 27001 scope must cover the cloud services in question. STAR Attestation combines a SOC 2 examination with the CCM and is performed by a CPA firm.
Which STAR Level Suits Your Organization?
Level 1 suits early-stage SaaS providers, firms answering their first enterprise questionnaires and teams that want a low-cost public baseline. Level 2 STAR Certification suits organizations that already hold ISO 27001 or sell mainly to buyers in Europe and Asia. Level 2 STAR Attestation suits providers whose clients are largely American and already expect a SOC 2 report. Many Manila companies start at Level 1 and move to Level 2 within a year or two.
Univate is a consultant. We are not a certification body or a CPA firm, and we do not issue certificates or attestation reports. We prepare you, then coordinate with the independent party you select.
Why Manila Businesses Invest in CSA STAR Certification
The most common trigger is a sales conversation that stalls. A bank in Makati, a multinational in Bonifacio Global City or an overseas client sends a cloud security questionnaire with hundreds of rows. Without a structured answer, your sales team waits weeks for engineers to respond. A STAR Registry entry lets buyers check your controls themselves and shortens that cycle.
Public policy points the same way. The Department of Information and Communications Technology (DICT) has a Cloud First policy that encourages government agencies to adopt cloud services. Providers hoping to serve agencies and government-owned corporations need a credible way to show their cloud controls. For many, CSA STAR certification in Manila becomes part of that story.
Trust is also visible. Because the STAR Registry is public, buyers, partners and even competitors can look up your listing. Being absent from it while rivals are present can quietly cost you deals.
CSA STAR, the Data Privacy Act and BSP Outsourcing Expectations
Cloud providers handling personal data of Filipino customers must meet the Data Privacy Act of 2012 (Republic Act 10173), enforced by the National Privacy Commission. The Act expects reasonable organizational, physical and technical security measures from both controllers and processors. Banks and other BSP-supervised institutions also apply BSP IT risk management and outsourcing expectations to their cloud providers. CSA STAR does not replace either regime. It does, however, give your clients and their regulators a detailed, control-by-control view of how you protect data in the cloud.
CSA STAR Requirements: What Your Organization Will Need
The CCM is broad, covering everything from application security to supply chain management. You do not need to be perfect in every domain to start. You do need a clear picture of your cloud services and honest, evidence-backed answers. These are the core preparation requirements for every CSA STAR certification in Manila that we support:
- A defined scope listing the cloud services, platforms and environments that STAR will cover
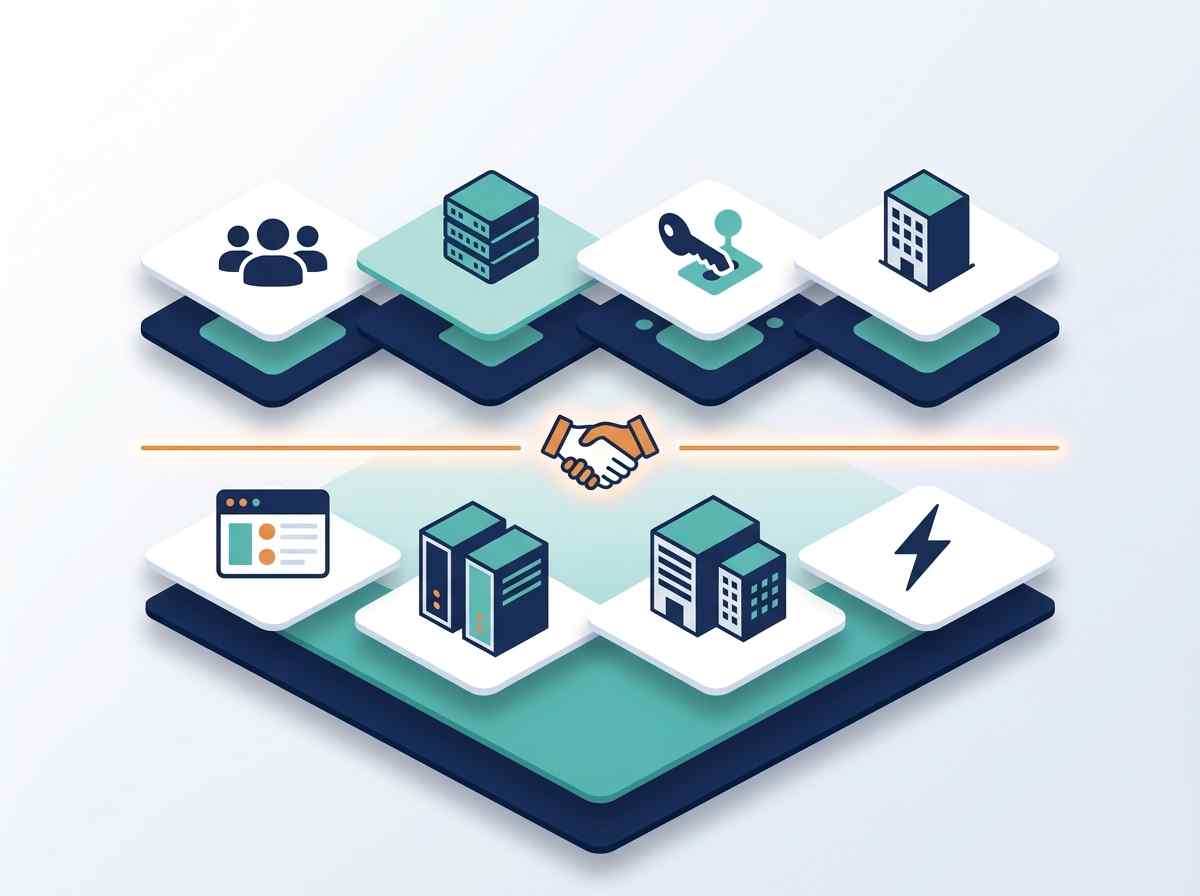
- A shared responsibility matrix showing which controls you own, which your cloud provider owns and which customers own
- A completed CCM gap assessment against v4.1, with a remediation plan for missing controls
- Security policies and procedures that match the CCM domains in scope, approved by management
- Evidence of key technical controls, such as access management, encryption key handling, logging and vulnerability management
- A completed CAIQ with clear, accurate explanations rather than one-word answers
- For Level 2, an ISO 27001 management system or a SOC 2 control environment that covers the same scope
Shared responsibility deserves special attention. Many Manila providers host on a major public cloud platform. That platform handles physical data center security, but your team still owns identity, configuration, application security and customer data handling. Auditors and buyers both want to see that line drawn precisely.
Accuracy matters more than optimism. Every “yes” on a CAIQ is a public claim. If a buyer later finds that a control does not work as described, the reputational damage outweighs any short-term sales benefit. We help you answer honestly and fix gaps before you publish.
Our CSA STAR Certification Process in Manila
We structure each engagement in six stages. The early stages are the same for every level. The later stages change depending on whether you are publishing a self-assessment or preparing for a Level 2 audit.
Step 1 – Level Selection and Service Scoping
We start by understanding your services, your customers and what they are asking for. Together, we decide which STAR level makes sense now and which one to target later. We then list the cloud services in scope and identify any existing ISO 27001 or SOC 2 work we can build on.
Step 2 – Cloud Controls Matrix Gap Assessment
Next, we compare your current controls with CCM v4.1, domain by domain. We look at policies, configurations, records and how your team actually operates. The output is a gap register that ranks each missing control by risk and effort, along with a shared responsibility map.
Step 3 – Remediation and Evidence Building
Your team closes the gaps with our guidance. That can mean writing policies, tightening cloud configurations, improving key management or setting up proper logging. We often recommend independent testing at this stage to confirm technical controls work as intended. We organize evidence so it is easy to retrieve during an audit or a customer review.
Step 4 – CAIQ Completion and Internal Review
We help you complete the CAIQ v4.1 with precise, defensible answers. Before anything is submitted or audited, we run an internal review that samples evidence behind each answer. Management signs off on the final version, since it represents the company’s public position.
Step 5 – STAR Registry Submission or Level 2 Audit
For Level 1, we support your submission of the completed CAIQ to the STAR Registry. For Level 2, a CSA-approved certification body audits your ISO 27001 system and CCM controls together. Alternatively, a CPA firm performs a SOC 2 examination that includes the CCM. We prepare your people for interviews, help schedule the audit and support your response to any findings.
Step 6 – Annual Renewal and CCM Version Transition
STAR is not a one-time exercise. Registry entries and Level 2 results need to be renewed every year to stay current. If you published on CCM v4, we plan your move to v4.1 well before the December 2027 cutoff. We also review changes to your cloud services, so your STAR listing keeps matching what customers actually buy.
Typical CSA STAR Timeline for Manila Organizations
The table below shows indicative durations for a single-platform SaaS or cloud provider. Actual timelines depend on the level, scope and how much existing ISO 27001 or SOC 2 work you already have.
| Phase | Key activities | Indicative duration | Main output |
|---|---|---|---|
| Level selection and scoping | Review customer demands, choose STAR level, list cloud services | 1–2 weeks | Scope statement and project plan |
| CCM gap assessment | Domain-by-domain review against CCM v4.1, shared responsibility mapping | 2–4 weeks | Gap register and responsibility matrix |
| Remediation | Policies, configuration changes, technical controls, evidence collection | 4–12 weeks | Implemented controls with records |
| CAIQ and internal review | Questionnaire completion, evidence sampling, management sign-off | 1–3 weeks | Approved CAIQ v4.1 |
| Submission or Level 2 audit | Registry submission, or certification body or CPA firm audit | 1–8 weeks, including scheduling | STAR Registry listing, certificate or attestation report |
A focused Level 1 project can often be completed in two to three months. Level 2 usually takes four to nine months, or less if a current ISO 27001 certificate or SOC 2 report already covers the same cloud services.
CSA STAR Certification in Manila: Cost and Timeline
There is no standard price list for CSA STAR, because the effort varies widely from one provider to the next. A start-up publishing its first CAIQ and a data center operator seeking Level 2 face very different workloads. These factors drive the cost of CSA STAR certification in Manila.
The STAR Level You Choose
Level 1 involves consulting effort and internal time but no external audit fee. Level 2 adds the cost of an independent audit, either by a CSA-approved certification body or by a CPA firm. The jump between the two is usually the single biggest cost difference.
Existing ISO 27001 or SOC 2 Work
If you already hold ISO 27001 certification, much of the groundwork for STAR Certification is in place. Likewise, a current SOC 2 report gives you a head start on STAR Attestation. Organizations starting from scratch must build that foundation first.
Cloud Services and Gap Size
Each additional platform, product or hosting environment in scope adds controls to check and evidence to collect. The size of your CCM gap matters just as much. A provider with mature access control, logging and key management needs far less remediation than one that has grown quickly without formal security processes.
Consulting and Auditor Fees
Your budget has two separate parts. The first is consulting support to assess, remediate and prepare. The second, for Level 2, is the auditor’s fee. It depends on scope, the number of services and whether the audit joins an existing ISO 27001 or SOC 2 cycle.
For STAR Certification, check that the certification body is approved by CSA. Its ISO 27001 certificates should be accredited by the Philippine Accreditation Bureau or another International Accreditation Forum member. For STAR Attestation, confirm the CPA firm is qualified to perform SOC 2 examinations. Once we understand your services, we provide an itemized quote that separates our fees from any third-party costs.
On timing, the biggest variable is usually internal. How quickly your engineers can change configurations, collect evidence and review drafts sets the pace. Projects move faster when one technical lead and one business owner are named at the start. If you also plan to pursue ISO 27001 for your wider organization, see our ISO 27001 certification in the Philippines service.
Benefits of CSA STAR Certification for Manila Businesses
Organizations that approach STAR as a real security program, not just a listing, tend to see benefits well beyond the sales team. These are the gains Manila providers usually notice first after CSA STAR certification in Manila.
Faster Answers to Cloud Security Questionnaires
A completed CAIQ becomes a ready-made response to many enterprise questionnaires. Instead of rebuilding answers for every prospect, your team points to the STAR Registry and handles only the remaining client-specific questions. That frees engineers to work on the product.
Public Visibility to Global Buyers
The STAR Registry is searchable by buyers around the world. A listing helps a Manila provider appear credible to procurement teams in markets where the company has no local presence or brand recognition yet.
A Clear Shared Responsibility Model
Mapping every control to you, your cloud provider or your customer removes confusion during incidents and contract talks. Customers understand what they must configure themselves, and your support team spends less time on disputes about who owns a problem.
Stronger Cloud Security Practice
Working through the CCM often uncovers practical weaknesses. Examples include unmanaged administrator accounts, encryption keys stored alongside data, missing log retention or untested restore procedures. Fixing these reduces the chance of breaches and outages, which matters in a city where monsoon flooding can disrupt on-premise equipment.
Reuse Across Other Frameworks
CCM controls map closely to ISO 27001, SOC 2 and privacy frameworks. The evidence you collect for STAR supports those programs too, including ISO 27701 privacy management. CSA has also introduced STAR for AI, which gives providers of AI services a path to build on the same foundation.
Why Manila Companies Choose Univate for CSA STAR
Univate has consulted more than 300 enterprises across cybersecurity and compliance. We have delivered over 1,000 audit man-days in critical infrastructure and regulated industries. Our consultants include CISA-certified professionals and specialists with decades of experience in security, risk and governance. We have also led more than 500 executive sessions on cybersecurity, AI governance and data privacy. That breadth helps us explain STAR choices clearly to founders, boards and engineering leads alike.
Our Philippine office is in Makati, a short trip from Manila’s main business districts. We understand the expectations of BSP-supervised clients, government buyers and overseas enterprises, and we tailor your STAR answers to each audience. Because we are a consultant and not an auditor, our only goal is to make you ready and keep the assessment independent.
We also design STAR work so it connects with your other compliance programs. Many cloud providers need a SOC 2 report for American clients and ISO 27001 for everyone else. We plan these together so evidence is collected once and reused. For multi-city operations, our CSA STAR certification in the Philippines service covers your full national footprint.
CSA STAR Certification in Manila: Services Across the City
We deliver CSA STAR certification in Manila through a hybrid model. Most gap reviews, CAIQ workshops and evidence checks happen remotely, which suits engineering teams that already work in cloud tools. We schedule on-site visits for scoping, data center walkthroughs and audit preparation.
Within the City of Manila, we work with organizations in Ermita and Malate, close to hospitals, government offices and the BSP head office. We support Binondo trading and distribution businesses moving order systems to the cloud. We also support Port Area and Tondo logistics firms running cloud-based tracking platforms. We also work with universities and education technology providers in Sampaloc and Intramuros, and with technology teams in Santa Mesa, Paco and Pandacan.
Beyond the city limits, we support cloud and SaaS companies in Makati, Bonifacio Global City in Taguig, Ortigas Center in Pasig, Pasay and Alabang. Wherever your engineers sit, you get the same structured approach and the same attention to accurate, defensible answers.
Planning CSA STAR certification in Manila?
Tell us about your scope, your sites and your timeline, and we will come back with a clear plan.
Client Testimonials
It was really a great partnership with their team.
Sultan
I had the pleasure and opportunity of working with Univate Solutions on a couple of High Maturity (ML5) CMMI appraisals and found them to be one of the best.
Amulya P
Team Univate holds many professional approaches.
Ashish Sherlekar
CSA STAR Certification in Manila: Frequently Asked Questions
What level of CSA STAR certification in Manila should we aim for first?
Most Manila providers start with Level 1, the CAIQ self-assessment, because it is quick and has no external audit fee. Move straight to Level 2 if your key customers already demand third-party assurance or you hold a current ISO 27001 certificate or SOC 2 report.
Is CSA STAR a legal requirement in the Philippines?
No. CSA STAR is voluntary. However, enterprise buyers, banks and government clients increasingly ask cloud providers for it, and its controls help you demonstrate the security measures expected under the Data Privacy Act.
Does Level 1 give us a certificate?
No. Level 1 is a public self-assessment listed on the STAR Registry. Only Level 2 STAR Certification results in a certificate, issued by a CSA-approved certification body. Level 2 STAR Attestation results in a SOC 2 report from a CPA firm.
Should we use CCM v4 or v4.1?
New projects should normally use CCM v4.1, released in January 2026. Submissions on v4 are accepted until December 2027, so existing v4 listings have time to transition. Plan the move during your next annual renewal.
We already have ISO 27001. How much extra work is STAR Certification?
Usually much less than a fresh project. Your ISO 27001 scope must cover the cloud services in question. You then add the CCM controls that your current system does not already address, and the certification body audits both together.
Can a Manila BPO use CSA STAR?
Yes, if it delivers services through a cloud platform it operates, such as a hosted contact center or analytics system. A BPO that only uses third-party cloud tools usually gains more from ISO 27001 or SOC 2.
How does shared responsibility affect our answers?
Some CCM controls are handled by your cloud provider, some by you and some by your customers. Your CAIQ answers should state clearly who owns each control. Claiming a provider’s control as your own is a common mistake that auditors and buyers notice.
How often do we need to update our STAR listing?
Plan to renew every year. You should also update your answers whenever your cloud services, hosting providers or key controls change significantly, so the public listing stays accurate.
Does Univate perform the Level 2 audit?
No. Univate is a consultant. The Level 2 audit is performed by a CSA-approved certification body for STAR Certification or by a CPA firm for STAR Attestation. We prepare you and coordinate with whichever independent party you choose.
Start Your CSA STAR Certification Project in Manila
Whether a buyer has asked for your STAR listing or you want a clearer way to explain your cloud security, the first step is a short conversation. We will review your services, recommend the right level and give you an itemized proposal for CSA STAR certification in Manila.
Book a Free Consultation Call +63 963 451 6528Prefer to talk first? Call our Philippines team on +63 963 451 6528, or send us your requirements through the contact form.
Email: info@univateglobal.com






