






SOC 2 Certification in Manila
Manila sits at the heart of Philippine banking, port trade and public administration. Its service firms also sell more and more to overseas buyers. Those buyers, especially in the United States, tend to ask one question early in procurement: can you share a SOC 2 report? SOC 2 certification in Manila is how local BPOs, software houses, logistics platforms and IT providers answer with independent evidence instead of another long security questionnaire.
Univate Global prepares Manila organizations for a SOC 2 examination against the AICPA Trust Services Criteria. We scope the systems and criteria your customers care about, design and test the controls, organize the evidence and coordinate with the independent CPA firm that performs the examination. Your team reaches fieldwork knowing what the auditor will request and where each record lives.
Every engagement starts from how your services actually run. A shared services center in Ermita supporting a US insurer carries different risks from a Port Area forwarder running a tracking portal. We shape the control set around your operations, contracts and available staff time.
Free ConsultationContact Us
Our Clients
SOC 2 Certification in Manila for BPOs, Financial Service Providers and Port Logistics Firms
SOC 2 was built for service organizations that run systems or processes on behalf of customers. If clients trust you with their data, uptime or transactions, it is relevant to you. In Manila, interest comes from a few distinct groups.
BPO and shared services operators lead the list. Delivery centers handle customer accounts, insurance claims, billing and technical support for US companies. Many of those clients push the same expectation down their vendor chain, and a current Type II report cuts renewal questionnaires. For healthcare accounts, SOC 2 often sits alongside HIPAA obligations.
Providers to banks and financial institutions form the second group. The Bangko Sentral ng Pilipinas has its head office in Malate, and the institutions it supervises scrutinize the IT vendors they rely on. Core banking software vendors, payment processors, fintech platforms, collection agencies and hosting providers are routinely asked for independent assurance, and SOC 2 gives a bank’s risk team exactly that.
Port and logistics businesses make up the third. Port Area is home to Manila South Harbor and the Manila International Container Terminal. Around them, and across the warehouses of Tondo, forwarders, customs brokers and logistics software firms run booking engines, tracking platforms and data exchanges for shippers. Global shippers increasingly want proof that these systems stay available and that shipment data remains accurate and confidential.
Software and SaaS companies, managed service providers, hospitals, universities and government contractors also approach us. Hospitals such as the Philippine General Hospital depend on outsourced IT and records partners. Universities in the University Belt run student systems through external vendors. Government contractors bidding for public or multinational projects are sometimes asked for an equivalent independent report.
How SOC 2 Certification Works in Manila
SOC 2 is a reporting framework from the American Institute of Certified Public Accountants (AICPA). A licensed CPA firm examines a service organization’s controls under the AICPA attestation standards known as SSAE 18, then issues a report containing its opinion. The yardstick is the Trust Services Criteria, issued in 2017 and refreshed with revised points of focus in 2022.
It helps to be precise about one thing. SOC 2 is an attestation report, not a certificate, and no certification body is involved. Most buyers still call it SOC 2 certification, so we use that phrase too. What your clients actually receive is the CPA firm’s report. Because SOC 2 reports are restricted-use documents, they are normally shared under a nondisclosure agreement.
Reports come in two types. A Type I report assesses whether your controls are suitably designed at a single point in time. A Type II report goes further and tests whether those controls operated effectively across an observation period, commonly three to twelve months. First Type II reports often use a shorter window of three to six months. Most enterprise buyers ultimately expect Type II.
SOC 1 covers controls relevant to customers’ financial reporting. SOC 3 is a general-use summary you can publish openly.
Univate is not a CPA firm and does not issue SOC reports. We prepare your organization, help you remediate gaps and coordinate with the CPA firm you appoint, whose independence gives its opinion weight.
Why Manila Businesses Invest in SOC 2 Certification
Much of Manila’s commercial life involves holding something on behalf of someone else. Banks hold deposits, forwarders hold cargo records, hospitals hold patient files and BPOs hold client accounts. When the client is a US company, its vendor risk team often begins with a request for a SOC 2 report. Without one, providers face repeated questionnaires and review calls, one client at a time.
Competition adds pressure. Manila providers compete for the same contracts as firms in Makati, Bonifacio Global City and Ortigas Center, and with vendors in other countries. Buyers comparing shortlisted suppliers tend to favor the one that can hand over an independent report on day one. For many local firms, SOC 2 certification in Manila turns a recurring sales obstacle into a standard document they send under NDA.
SOC 2, the Data Privacy Act and BSP Expectations
The Data Privacy Act of 2012 (Republic Act 10173), enforced by the National Privacy Commission, requires personal information controllers and processors to apply organizational, physical and technical security measures. A SOC 2 program covering Security, and optionally Privacy, maps well onto those measures and produces dated evidence that they work. It does not, however, prove compliance with the Act on its own. Local duties such as appointing a Data Protection Officer and notifying the NPC of qualifying breaches within 72 hours still need attention. For a privacy management system recognized internationally, many firms pair SOC 2 with ISO 27701.
Providers serving BSP-supervised banks have a further reason. Those institutions are expected to manage IT and outsourcing risk carefully, including oversight of their service providers. A current SOC 2 report gives a bank’s compliance and audit teams concrete material for that oversight, which can shorten onboarding and annual vendor reviews.
SOC 2 Requirements: What Your Organization Will Need
The AICPA does not hand you a fixed checklist. Instead, you choose which Trust Services Criteria categories fall within the examination, then design controls that satisfy each criterion in your own environment. Every SOC 2 report covers Security. The other four categories are added when your customer commitments call for them:
- Security, also called the common criteria: protection of systems and data against unauthorized access, disclosure and damage. It is always included.
- Availability: systems are available for operation and use as committed in your contracts and service level agreements.
- Processing Integrity: system processing is complete, valid, accurate, timely and authorized.
- Confidentiality: information designated as confidential is protected throughout its life cycle as committed or agreed.
- Privacy: personal information is collected, used, retained, disclosed and disposed of in line with your stated commitments.
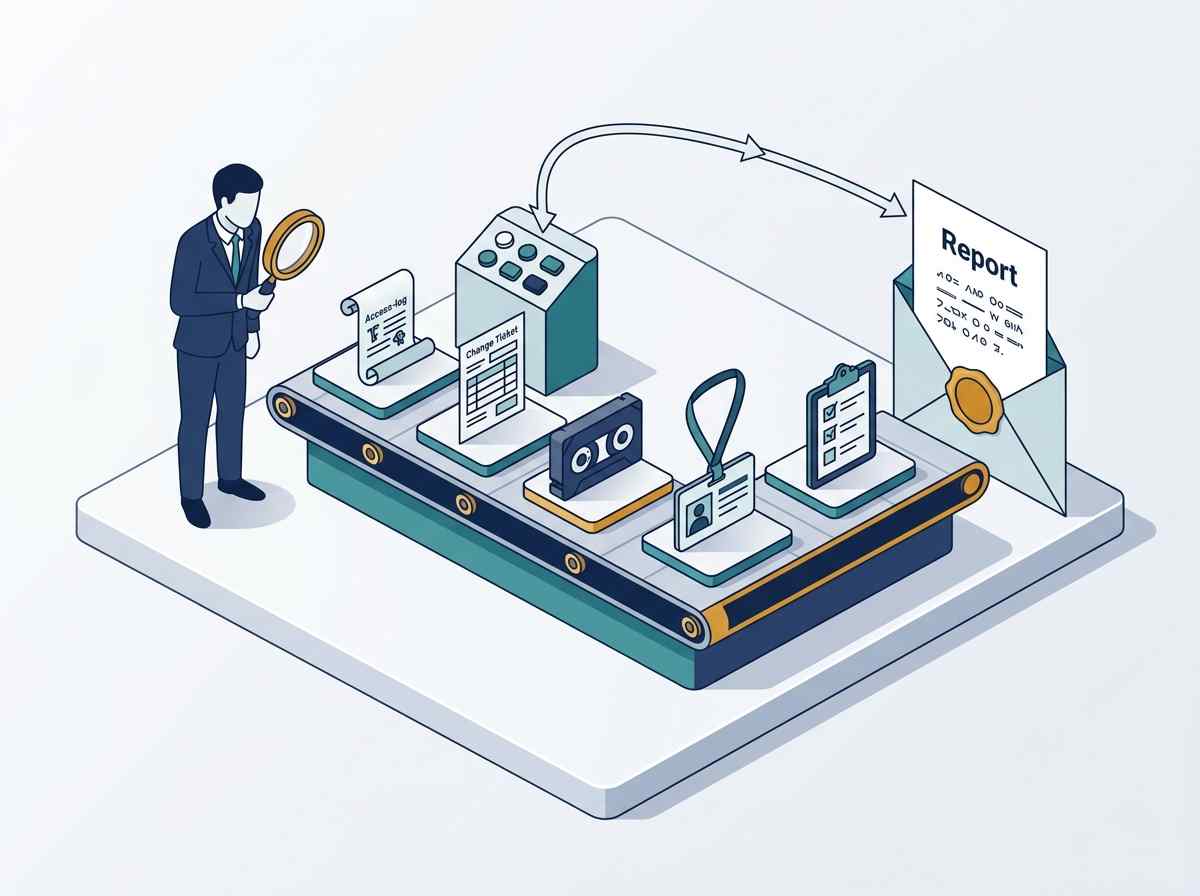
Behind those categories sit practical controls. Expect to evidence a risk assessment, documented policies, periodic user access reviews, change management for code and infrastructure, logging and monitoring, vendor management, incident response, onboarding and offboarding, and security awareness. You will also prepare a system description covering your services, infrastructure, people, data and boundaries.
For a Type II report, the bar is consistency. The auditor samples tickets, approvals, alerts and review records from across the observation period. A control that worked in March but lapsed in June becomes an exception in the report. We therefore help you assign clear owners and simple routines so that evidence builds up as part of normal work, not in a rush before fieldwork.
Our SOC 2 Certification Process in Manila
We run SOC 2 certification in Manila as six connected stages. Each stage has defined outputs, so your leadership always knows what is complete, what is next and what your team must supply.
Step 1 – Readiness Assessment and Scoping
We start by learning which services your customers buy, which systems support them and what your contracts promise. Then we recommend the Trust Services Criteria to include and whether to begin with Type I or go straight to Type II. A readiness assessment then compares your current practices with each criterion and produces a prioritized gap list.
Step 2 – Risk Assessment and Control Design
Next, we work with your team to identify the risks that could stop you meeting your service commitments. We then design or refine controls that answer each risk and each applicable criterion. The output is a control matrix that links every control to its owner, its frequency and the evidence it will generate.
Step 3 – Policies, Remediation and Control Rollout
We draft or update the policies the controls depend on and help your teams close the gaps. Typical work includes tightening access management, formalizing change approvals, centralizing logs, documenting vendor reviews and rehearsing incident response. Where customers expect technical testing, we can coordinate vulnerability assessment and penetration testing.
Step 4 – Evidence Collection and Pre-Audit Review
Before the CPA firm arrives, we test your controls the way an auditor would, sampling evidence and flagging likely exceptions. We also help finalize the system description and prepare interviewees.
Step 5 – CPA Firm Type I or Type II Examination
The independent CPA firm you appoint performs the examination. For Type I, it assesses control design as of a chosen date. For Type II, it tests operating effectiveness across the agreed observation period, then issues its report after fieldwork. We coordinate requests, track open items and help your team respond clearly to auditor questions.
Step 6 – Annual Renewal and Continuous Monitoring
Customers usually expect a fresh report every 12 months, so SOC 2 is a recurring cycle rather than a one-off project. We help you keep controls running between examinations through periodic reviews and evidence checks. Where a gap opens between report periods, your CPA firm’s bridge letter can cover it while the next report is prepared.
Typical SOC 2 Timeline for Manila Organizations
The table below gives indicative durations for a small or mid-sized service organization with a single main system. Real timelines depend on scope, criteria and current maturity.
| Phase | Key activities | Indicative duration | Main output |
|---|---|---|---|
| Readiness and scoping | Map services and systems, select criteria, compare practices to criteria | 2–3 weeks | Scope statement and gap report |
| Control design | Risk assessment, control matrix, owner assignment | 2–4 weeks | Approved control matrix |
| Remediation and rollout | Policies, access, change, logging, vendor and incident controls | 6–12 weeks | Operating controls with evidence |
| Pre-audit review | Evidence sampling, system description, interview preparation | 2–3 weeks | Readiness sign-off |
| Type I examination | CPA firm assesses control design at a point in time | A few weeks, including scheduling | SOC 2 Type I report |
| Type II observation and examination | Controls operate and are tested over the period | 3–12 months, plus reporting time | SOC 2 Type II report |
Most Manila service providers can reach a Type I report within three to five months of starting. A first Type II report typically follows after a three- to six-month observation period and the CPA firm’s reporting time. Multi-site operations or those starting with few formal controls should plan for longer.
SOC 2 Certification in Manila: Cost and Timeline
SOC 2 pricing varies widely because no two scopes are alike. A sensible budget comes from understanding what the report must cover and who needs to read it. These are the factors that shape the investment.
Report Type and Observation Period
A Type I report involves less testing and less time than a Type II. A Type II with a twelve-month observation period requires sustained evidence and more auditor sampling than one covering three months. Many companies spread the cost by starting with Type I and moving to Type II the following cycle.
Trust Services Criteria in Scope
Security alone is the leanest scope. Adding Availability, Processing Integrity, Confidentiality or Privacy brings more controls to design, more evidence to keep and more for the CPA firm to test. We recommend including only the categories your customers actually rely on.
Systems, Cloud Platforms and Vendors
The number of applications, environments and locations in scope drives effort. So does reliance on outside providers, such as cloud hosting, payroll or managed security services. Their own SOC reports, and how your report treats them, affect both preparation and testing.
Consulting Fees and CPA Firm Fees
Your total cost has two separate parts. The first is consulting support to prepare your controls and evidence. The second is the CPA firm’s examination fee, which the firm sets based on report type, criteria and complexity. Compliance automation tools, if you choose to use one, are a third optional line item.
There is no accreditation body for SOC 2 in the ISO sense. What matters is that a licensed CPA firm issues the report under AICPA attestation standards. Ask your largest customers whether they prefer particular firms. Once we understand your scope, we provide an itemized quote for our part of the work.
On timing, the main variable is your observation period, followed by how quickly your team can fix gaps and produce evidence. Organizations with a mature security program often reach Type II within six to nine months of starting. For national scope across several Philippine sites, see our SOC 2 in the Philippines service.
Benefits of SOC 2 Certification for Manila Businesses
The value of SOC 2 certification in Manila shows up in sales, operations and governance. Most organizations see results within the first full report cycle.
Shorter Security Reviews With US Clients
A current report answers most of the questions a US vendor risk team would otherwise send in a spreadsheet. Sales teams spend less time on questionnaires, and renewals move with fewer delays.
Stronger Standing With Banks and Regulated Buyers
Banks, insurers and healthcare organizations need defensible reasons to trust their providers. An independent CPA opinion gives their auditors something solid to file. For vendors serving institutions supervised from the BSP’s Malate head office, that credibility matters in every tender.
Reliable Service Through Monsoon Floods and Outages
Monsoon flooding and power interruptions are a fact of life in Manila. Including the Availability criterion pushes you to test backups, document recovery steps and monitor capacity. The result is a service that keeps its promises when roads close and offices empty, with evidence to show clients.
Clear Ownership and Cleaner Evidence
SOC 2 requires named control owners, regular reviews and records that prove they happened. Over time, this replaces informal habits with routines that survive staff turnover.
Why Manila Companies Choose Univate for SOC 2
Univate has consulted more than 300 enterprises across cybersecurity and compliance and has delivered over 1,000 audit man-days across critical infrastructure and regulated industries. Our consultants include CISA-certified professionals and specialists with decades of experience in security, risk and governance. Our Philippine office is in Makati, a short drive from Manila’s banking, port and university districts. That mix of audit discipline and local presence shapes how we deliver SOC 2 certification in Manila.
We are your consultant, never your auditor, so our advice is not tied to any CPA firm’s fee. We build controls around tools you already use, such as your cloud platform, ticketing system and identity provider, so evidence comes from normal work.
Manila clients often face more than one framework at once. A payment processor may need PCI DSS as well, while a bank vendor may also be asked for ISO 27001. We design a single control set that serves several frameworks, so you avoid duplicated effort.
SOC 2 Certification in Manila: Services Across the City
We support organizations throughout the City of Manila using a hybrid model. Workshops, document reviews and evidence checks mostly run remotely. On-site visits are planned around key milestones, such as the readiness assessment, the pre-audit review and the start of CPA fieldwork.
Within the city, we work with financial service providers and health-tech vendors in Ermita and Malate, and with trading and distribution companies in Binondo. In Port Area and Tondo, we support forwarders, customs brokers and logistics software firms tied to the South Harbor and the container terminal. We also work with education technology providers and university service partners in Sampaloc, Intramuros and Santa Mesa, plus businesses in Paco and Pandacan.
Many Manila clients have offices or customers in neighboring business districts too. We support organizations in Makati, Bonifacio Global City in Taguig, Ortigas Center in Pasig, Pasay and Entertainment City, and Alabang. The same structured method applies wherever your systems and people sit.
Planning SOC 2 certification in Manila?
Tell us about your scope, your sites and your timeline, and we will come back with a clear plan.
Client Testimonials
It was really a great partnership with their team.
Sultan
I had the pleasure and opportunity of working with Univate Solutions on a couple of High Maturity (ML5) CMMI appraisals and found them to be one of the best.
Amulya P
Team Univate holds many professional approaches.
Ashish Sherlekar
SOC 2 Certification in Manila: Frequently Asked Questions
How long does SOC 2 certification in Manila take from start to report?
A Type I report is usually achievable within three to five months, depending on your starting point. A Type II report adds an observation period, commonly three to six months for a first report, plus reporting time. Many organizations therefore receive their first Type II report six to nine months after starting.
Will we receive a SOC 2 certificate?
No. SOC 2 results in an attestation report containing the CPA firm’s opinion, not a certificate. Buyers still describe it as certification, but what you share with them is the report itself, normally under an NDA.
Should we start with a Type I or a Type II report?
If a client deal is waiting, a Type I report can show well-designed controls quickly. If buyers already insist on Type II, it often makes sense to begin the observation period as soon as controls are operating. We help you weigh deadlines against cost.
Can Univate issue our SOC 2 report?
No. Only a licensed CPA firm can perform the examination and issue the report. Univate prepares your organization, manages the evidence process and coordinates with the firm you choose, which keeps the examination independent.
Do we need to include all five Trust Services Criteria?
No. Security is always required. Availability, Processing Integrity, Confidentiality and Privacy are added only when your service commitments or customer contracts make them relevant. A narrower, well-chosen scope is usually stronger than a broad, thin one.
A bank client asked for SOC 1. Is that the same as SOC 2?
Not quite. SOC 1 covers controls relevant to a customer’s financial reporting, such as transaction processing that feeds their books. SOC 2 covers security and related criteria. Some providers to Manila banks need one, the other, or both.
How does SOC 2 compare with ISO 27001?
SOC 2 is an attestation report most often requested by US buyers. ISO 27001 is a certification recognized worldwide. Their controls overlap heavily, so organizations with clients in several regions often maintain both from one program.
Does a SOC 2 report make us compliant with the Data Privacy Act?
Not by itself. SOC 2 certification in Manila supports the security measures the Act requires and can include a Privacy category. However, local obligations such as DPO appointment and breach notification to the National Privacy Commission still need separate attention.
What happens when our report becomes more than a year old?
Customers usually expect a new report every 12 months. Between report periods, your CPA firm can issue a bridge letter covering the gap. Keeping controls running continuously makes each renewal faster and avoids surprises.
Start Your SOC 2 Certification Project in Manila
Whether a US client has asked for your report or a bank has added SOC 2 to its vendor requirements, the first step is a short conversation. We will discuss your services, systems and deadlines, recommend a sensible scope and report type, and send an itemized proposal for SOC 2 certification in Manila.
Book a Free Consultation Call +63 963 451 6528Prefer to speak with someone first? Call our Philippines team on +63 963 451 6528, or share your requirements through the contact form.
Email: info@univateglobal.com






