






ISO 27001 Certification in Manila
Manila sits at the center of Philippine trade, finance, healthcare and government. Shipping lines, banks, hospitals and their service providers exchange sensitive data every hour. ISO 27001 certification in Manila shows clients, regulators and partners that your organization protects that information through a managed, audited system.
Univate Global helps organizations in the capital build an Information Security Management System (ISMS) that conforms to ISO/IEC 27001:2022. Our consultants handle the heavy lifting with your team. That covers scoping, risk analysis, policy writing, control rollout, internal audit and preparation for the external certification audit.
Your operation might be a freight forwarder near the Port Area, a trading house in Binondo or a clinic group in Ermita. It might also be a shared services team serving a bank in Malate. Either way, the ISMS we build mirrors how your Manila teams already move cargo, money or patient files. The goal is a system your staff can run confidently long after the auditor leaves.
Free ConsultationContact Us
Our Clients
ISO 27001 Certification in Manila for Logistics, Finance and Healthcare
Information security matters to every sector, but three groups in the city drive most requests for an accredited ISMS.
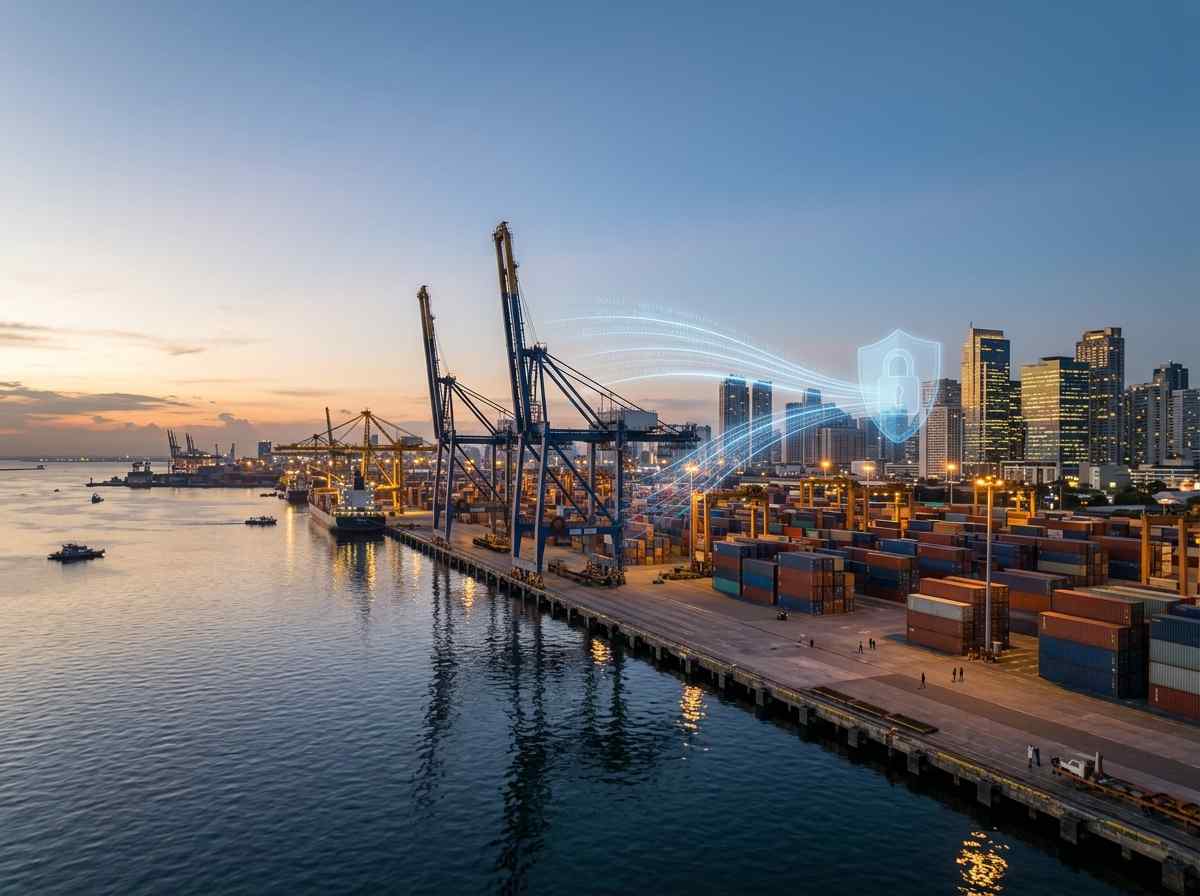
Ports and logistics come first. Manila South Harbor and the Manila International Container Terminal anchor a dense logistics network. Forwarders, customs brokers, truckers and warehouses cluster in the Port Area and Tondo. These firms hold shipping manifests, consignee details, customs filings and pricing data. Global shipping lines and cargo owners now review their partners’ security before sharing system access.
Banking and financial services form the second group. The Bangko Sentral ng Pilipinas has its head office in Malate, and BSP-supervised institutions operate under its IT risk management regulations. Banks, remittance companies, lenders and payment firms pass those expectations down to their technology vendors and outsourcing partners. An ISO 27001 certificate gives those suppliers a recognized way to answer.
Healthcare is the third. Hospitals around Ermita and Malate, including the Philippine General Hospital, handle patient histories, laboratory results and billing records. Diagnostic centers, health maintenance organizations and medical billing firms also manage health data that is highly sensitive under the Data Privacy Act.
Demand is also growing beyond these three groups. Binondo trading and distribution companies, universities in the University Belt and Intramuros, and hotels in Ermita and Malate all ask about it. So do BPOs serving overseas accounts. Government contractors and printing and publishing firms that process confidential documents also ask about certification.
Company size is rarely a barrier. A 15-person customs brokerage can certify a tightly defined scope. A multi-floor contact center can certify a much larger one. The workload simply follows the boundaries you choose.
How ISO 27001 Certification Works in Manila
ISO/IEC 27001 is the international standard that specifies requirements for an information security management system. ISO and the International Electrotechnical Commission publish it jointly. In plain terms, it asks you to understand your information risks, choose sensible controls, and keep the whole system under regular review.
Since October 2025, the 2013 version can no longer be certified. Every audit in Manila now runs against ISO/IEC 27001:2022. Its Annex A lists 93 controls arranged in four themes: organizational, people, physical and technological. Controls added in 2022 include threat intelligence, cloud services security, data masking, data leakage prevention and secure coding. For a forwarder sharing booking data with carriers, leakage prevention alone can reshape daily routines.
Two separate parties are involved, and the distinction matters. Univate is the consultant that helps you build and rehearse the ISMS. An accredited certification body later sends its own auditors, who alone decide whether a certificate is granted. Keeping advice and assessment apart is what gives ISO 27001 certification in Manila its value to buyers.
Why Manila Businesses Invest in ISO 27001 Certification
Most Manila organizations pursue certification because a customer asked for it. Multinational shippers, foreign principals of trading houses and overseas BPO clients send long security questionnaires during onboarding. A valid certificate from an accredited body covers much of that ground. It also signals that an independent auditor has already tested your controls.
Local competition adds pressure. Firms in Manila bid against providers in Makati, Bonifacio Global City and Ortigas Center, as well as regional hubs abroad. When proposals look similar on price and capability, ISO 27001 certification in Manila often decides the shortlist.
There is also a practical motive. Ransomware, phishing and insider data leaks affect companies of every size in the metro. A structured ISMS forces leadership to fund the controls that matter, rather than reacting after an incident.
The Data Privacy Act and the National Privacy Commission
Under Republic Act 10173, the Data Privacy Act of 2012, anyone controlling or processing personal data must apply organizational, physical and technical safeguards. The National Privacy Commission enforces the law and investigates breaches. For a Manila hospital, bank vendor or shipping agent, ISO 27001 turns those safeguards into a managed, evidenced routine. It does not cover every privacy duty, such as lawful basis, consent and data subject rights. Still, it supplies much of the security proof the Commission and your clients will expect.
ISO 27001 Requirements: What Your Organization Will Need
ISO 27001 defines outcomes and leaves the methods to you. A Binondo wholesaler and a Malate payment startup will satisfy identical clauses with very different controls. Even so, every project for ISO 27001 certification in Manila must produce certain elements. Auditors will check for each of these:
- A documented scope listing the offices, warehouses, teams, systems and services inside the ISMS
- Leadership-approved security policy and objectives that can be measured
- A defined method for assessing and treating information security risks, with recorded results
- A Statement of Applicability justifying the inclusion or exclusion of each Annex A control
- Working procedures for areas such as user access, supplier security, incidents, backups and system changes
- Evidence of training, security awareness and staff competence
- Internal audit results, management review minutes and tracked corrective actions
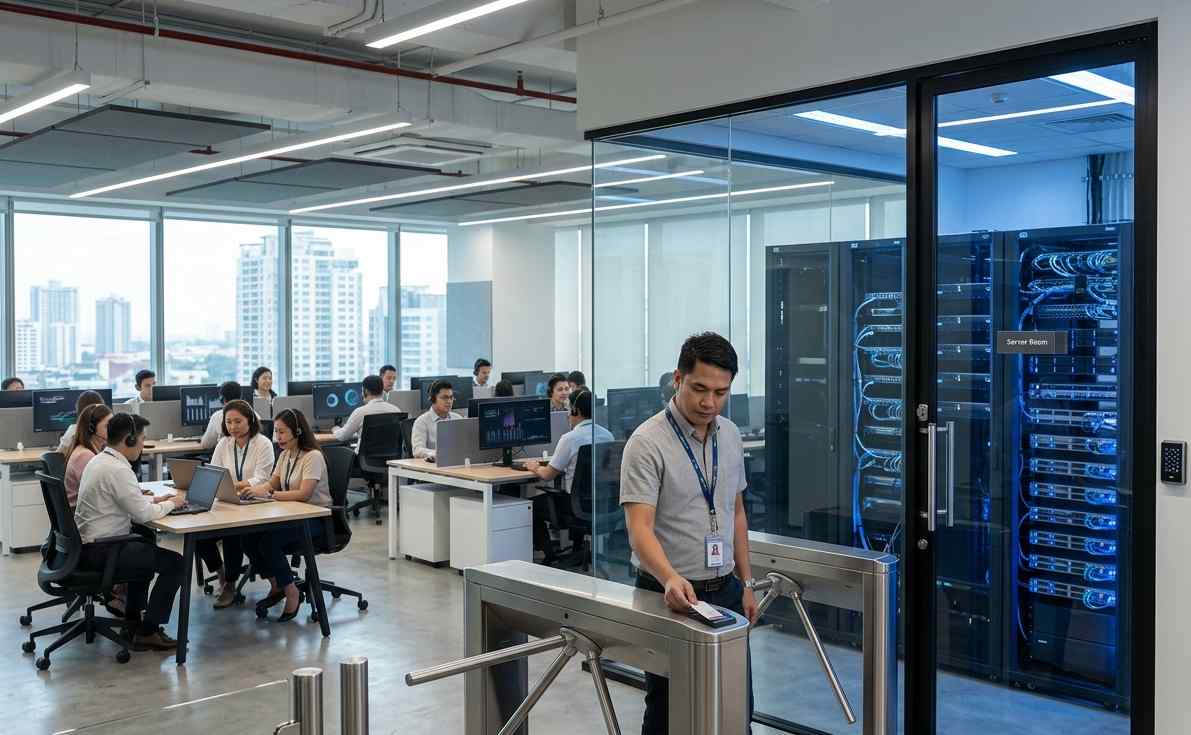
Reading your manuals is only the start for an auditor. Expect them to question dispatch clerks, developers, nurses or tellers, depending on scope, and to pull real records. If a procedure says access is reviewed every quarter, they will want to see the last review. We therefore spend as much effort on building habits and records as on drafting policies.
Management commitment is a formal requirement, not a courtesy. Executives have to set direction, fund the work and review progress. Schedules hold best when a single senior sponsor is accountable for the result. A small working group from IT, operations and compliance then carries the daily tasks with our consultants.
Our ISO 27001 Certification Process in Manila
Our method for ISO 27001 certification in Manila runs in six stages. You see the plan from day one, with clear owners, deliverables and decision points for each stage.
Step 1 – Readiness Review and Scope Definition
We compare your existing controls, documents and practices against each clause and Annex A control. Conversations with dispatchers, IT staff and managers reveal how work actually flows. We then agree on a scope that serves your commercial aims. It might be one warehouse in Tondo, a single client program or the whole Manila operation.
Step 2 – Risk Analysis and Treatment Decisions
Together we list the information assets that matter, from customs databases to patient records and trading ledgers. We examine the threats and weaknesses that could affect each one. Every risk receives a rating, an owner and a treatment decision. Those decisions feed directly into your Statement of Applicability.
Step 3 – Policy Development and Control Rollout
We prepare policies and procedures in plain language that your staff will actually read. Controls are built into the tools you already run, whether that is Microsoft 365, Google Workspace, an ERP or a cloud platform. We also deliver awareness sessions so employees know how to spot phishing, report incidents and handle data correctly.
Step 4 – Internal Audit and Leadership Review
Once the system has run for a period, our auditors test it end to end, just as the certification body will. We record findings, help you correct them and guide your executives through the required management review. This rehearsal usually reveals the gaps that would otherwise surface in the real audit.
Step 5 – External Audit in Two Stages
Your chosen certification body conducts a Stage 1 audit to confirm documentation and readiness. A Stage 2 audit follows, often several weeks later, to test whether controls work in daily operation. We brief your team before each stage and support you in answering any nonconformities raised.
Step 6 – Surveillance Years and Recertification
Certificates last three years. Surveillance audits take place in years one and two, and a full recertification audit comes in year three. We can continue as your ongoing partner, running internal audits, refreshing risk assessments and updating controls as your business changes.
Typical ISO 27001 Timeline for Manila Organizations
The durations below reflect a typical single-site organization with modest complexity. Your own schedule will depend on scope, staff numbers and the controls already in place.
| Phase | Key activities | Indicative duration | Main output |
|---|---|---|---|
| Readiness review and scoping | Clause-by-clause review, staff interviews, scope agreement | 1–2 weeks | Readiness report and project roadmap |
| Risk analysis | Asset inventory, threat and weakness review, treatment choices | 2–3 weeks | Risk register, treatment plan, Statement of Applicability |
| Policy and control rollout | Policies, procedures, technical controls, awareness training | 6–12 weeks | Operating ISMS with evidence |
| Internal audit and leadership review | Full internal audit, corrections, management review | 2–3 weeks | Internal audit report and resolved findings |
| Certification audits | Stage 1 and Stage 2 by an accredited certification body | 2–6 weeks, including scheduling | ISO/IEC 27001:2022 certificate |
In practice, small and mid-sized Manila organizations typically reach certification in three to six months. Operations spread across several sites, running round-the-clock shifts or starting from very limited controls should plan for six to nine months.
ISO 27001 Certification in Manila: Cost and Timeline
Because every scope differs, a responsible consultant cannot quote a single standard price. The budget depends on how much of your organization the ISMS covers and how mature your current controls are. Four factors shape the figure most.
People and Processes in Scope
The number of employees and contractors inside the scope drives both consulting time and audit duration. A tightly scoped service line costs less to implement and audit than an entire company.
Number of Locations
A head office in Ermita plus warehouses in Tondo and Pandacan requires more coordination than one floor in a single building. Auditors may need to visit or sample several sites, and controls must work consistently in each.
Systems, Cloud and Outsourced Services
Organizations running their own servers, several cloud platforms, custom software or many outsourced IT providers have more to assess and control. A company that relies on a few well-configured SaaS tools usually has a lighter path.
Consulting Effort Versus Audit Fees
Your budget has two distinct parts. Consulting fees cover the work of building and preparing the ISMS. Certification body fees cover the Stage 1, Stage 2 and surveillance audits. The certification body sets audit days using ISO/IEC 27006, mainly from headcount and complexity.
Pick a certification body holding accreditation from the Philippine Accreditation Bureau or another International Accreditation Forum (IAF) member. Accredited certificates carry weight with foreign principals and multinational buyers. After a short scoping call, we provide an itemized quote that separates every element of our consulting work.
On timing, most single-site Manila organizations with 20 to 200 staff are audit-ready within three to six months. Internal availability is the usual bottleneck, especially how quickly reviewers approve documents and teams produce evidence. Our ISO 27001 certification cost breakdown explains the budget drivers in more detail.
Benefits of ISO 27001 Certification for Manila Businesses
A well-run ISMS pays back in ways that reach beyond the certificate itself. Companies that complete ISO 27001 certification in Manila typically report commercial, operational and governance gains.
Smoother Onboarding With Global and Financial Clients
An accredited certificate often replaces dozens of questionnaire answers for shipping lines, foreign principals and banks. That shortens vendor onboarding and reduces repeated client audits. It also helps renewals, because you can show surveillance audit results each year.
Reduced Exposure to Breaches and Fraud
Risk assessment brings hidden weaknesses into view. Examples include shared accounts at a warehouse terminal, unencrypted laptops leaving a branch, or vendors with standing remote access. Addressing them methodically lowers the chance and impact of ransomware, fraud and data leaks.
Continuity Through Monsoon Floods and Outages
Manila’s monsoon season regularly brings flooding that can close offices, disrupt power and cut connectivity. ISO 27001 requires you to plan for information security during disruption, including backups and alternative ways of working. If clients demand a formal continuity program, the same groundwork extends naturally to ISO 22301 business continuity.
Clear Ownership at Leadership Level
Every risk and control gets a named owner, internal audits run on a calendar, and executives review results formally. Security stops being an informal task for one IT administrator. It becomes a governed program with measurable objectives and regular reporting to management.
A Reusable Base for Other Frameworks
Controls built for ISO 27001 overlap heavily with ISO 27701, PCI DSS and SOC 2 reporting. Starting with a solid ISMS means later frameworks reuse existing policies, evidence and risk work. That avoids building separate compliance programs from scratch.
Why Manila Companies Choose Univate for ISO 27001
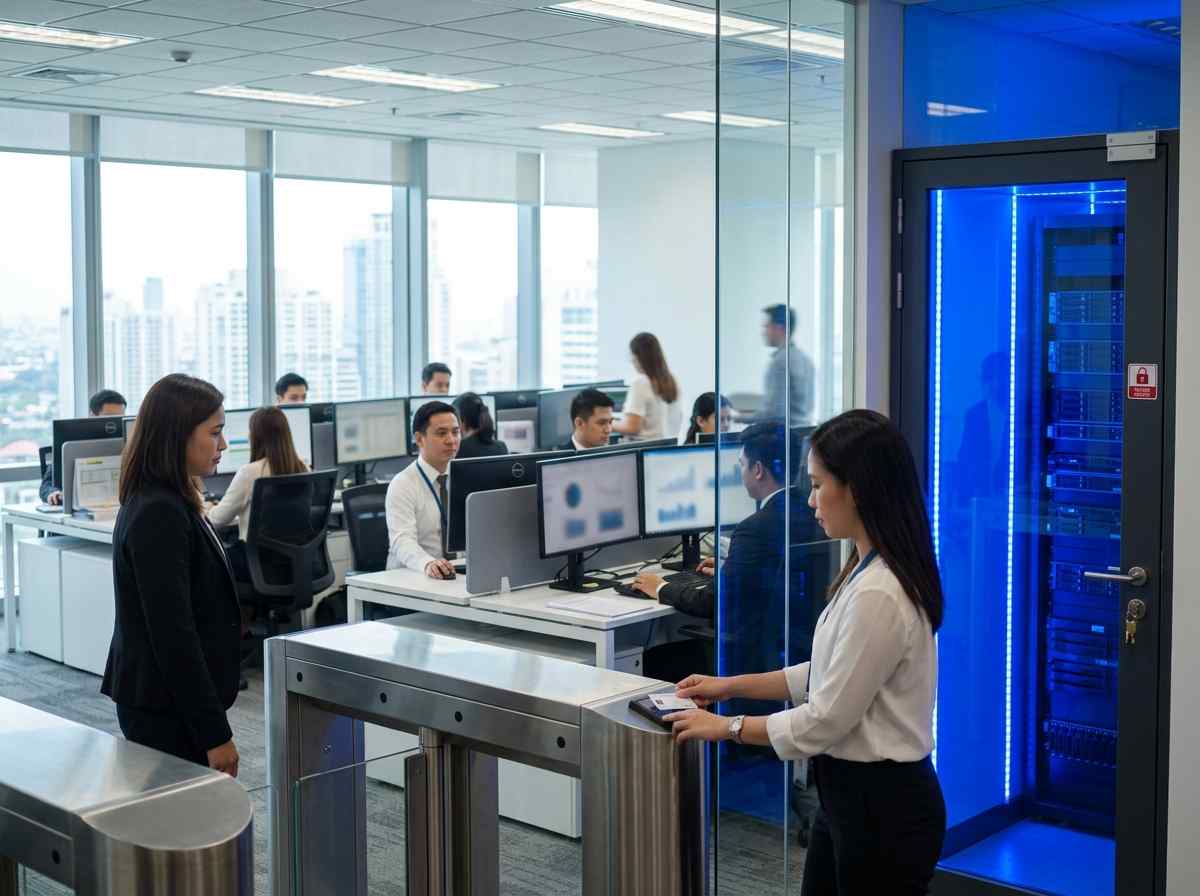
Univate has consulted over 300 enterprises in cybersecurity and compliance. We have logged more than 1,000 audit man-days in critical infrastructure and regulated sectors. We have also led over 500 executive sessions on cybersecurity, AI governance and data privacy. The team brings together CISA-certified professionals, CMMI lead appraisers and specialists with decades in quality, security, risk and governance. Univate’s Philippine office sits next door in Makati, which keeps us close to clients pursuing ISO 27001 certification in Manila.
We design each ISMS to match how your organization works. Policies reflect your actual processes, approval chains and systems, so they remain useful after the audit. Where technical assurance is needed, we can add vulnerability assessment and penetration testing. As a consultant rather than a certifier, we stay focused on your readiness while the audit remains fully independent.
Many Manila organizations also run branches, warehouses or delivery teams elsewhere in the country. Our nationwide ISO 27001 program can bring those locations into a single, coordinated scope.
ISO 27001 Certification in Manila: Services Across the City
We deliver every project through a hybrid model. Workshops, document reviews and status meetings run remotely to save your team time. Our consultants visit on site for key milestones, such as the readiness review, the internal audit and final audit preparation.
Within the City of Manila, we support logistics and port-related businesses in the Port Area and Tondo, and trading and wholesale companies in Binondo. We work with hospitals, hotels and professional firms in Ermita and Malate, and with educational institutions in Intramuros and the University Belt in Sampaloc. We also support organizations in Santa Mesa, Paco and Pandacan, including distributors, food and beverage companies and printing and publishing firms.
Our consultants also work with organizations across Metro Manila. That includes Makati, Bonifacio Global City in Taguig, Ortigas Center in Pasig, Pasay and Entertainment City, and Alabang. For teams based north of the city, see our page on ISO 27001 certification in Quezon City. Companies with Visayas operations can review ISO 27001 certification in Cebu. For our full range of services, visit Univate Philippines.
Planning ISO 27001 certification in Manila?
Tell us about your scope, your sites and your timeline, and we will come back with a clear plan.
Client Testimonials
It was really a great partnership with their team.
Sultan
I had the pleasure and opportunity of working with Univate Solutions on a couple of High Maturity (ML5) CMMI appraisals and found them to be one of the best.
Amulya P
Team Univate holds many professional approaches.
Ashish Sherlekar
ISO 27001 Certification in Manila: Frequently Asked Questions
How many months should we plan for ISO 27001 certification in Manila?
Plan for three to six months if you are a single-site organization of small or medium size. Larger scopes, several locations or 24/7 operations commonly need six to nine months. The pace depends heavily on how quickly your team reviews documents and produces evidence.
Is ISO 27001 a legal requirement for Manila companies?
No law in the Philippines makes ISO 27001 itself compulsory. However, clients, principals and partners frequently write it into contracts. The Data Privacy Act also requires appropriate security measures for personal data, and an ISO 27001 ISMS is a strong way to demonstrate them.
Who grants the certificate, Univate or an auditor?
An independent certification body grants it after auditing your ISMS. Univate prepares you for that audit but never issues certificates. We can help you shortlist bodies accredited by the Philippine Accreditation Bureau or another IAF member.
We still hold a 2013-edition certificate. Is it valid?
The transition period for ISO/IEC 27001:2013 ended in October 2025. Certificates against the older edition are no longer valid. If your organization missed the transition, you will need to certify against ISO/IEC 27001:2022.
Should we choose ISO 27001 or SOC 2?
Look at where your clients sit. American buyers tend to ask for SOC 2, an AICPA attestation that only a licensed CPA firm can issue. European, Asian and Australian buyers usually prefer ISO 27001. Shared controls make holding both realistic for Manila BPOs with mixed client bases.
Can we certify just one warehouse or business unit?
Yes. You can define a scope that covers one site, department, client program or service. A Tondo warehouse or a single Ermita clinic is a sensible first scope, and more sites can join at later audits.
Does ISO 27001 make us compliant with the Data Privacy Act?
Not entirely. ISO 27001 addresses the security safeguards the Act expects, and it produces useful evidence for the National Privacy Commission. Other duties, such as consent, lawful processing and data subject rights, need separate attention.
How much staff time does the project require?
Expect a senior sponsor to give a few hours each month and a small working group to commit regular weekly time. Most other employees attend awareness training and follow updated procedures. Our consultants carry most of the drafting and audit preparation.
What happens after we receive the certificate?
Your certificate runs for three years. Surveillance audits follow in the first and second years, then recertification in the third. Between audits, you keep running risk reviews, internal audits and management reviews to show continual improvement.
Start Your ISO 27001 Certification Project in Manila
The best starting point is a short conversation about your clients, scope and deadlines. We will gauge your readiness, recommend a workable scope and prepare an itemized proposal for ISO 27001 certification in Manila. There is no cost for the initial consultation.
Book a Free Consultation Call +63 963 451 6528Prefer a phone call? Reach our Makati-based Philippines team on +63 963 451 6528, or send your details through the contact form.
Email: info@univateglobal.com






