






GDPR Certification in Cebu
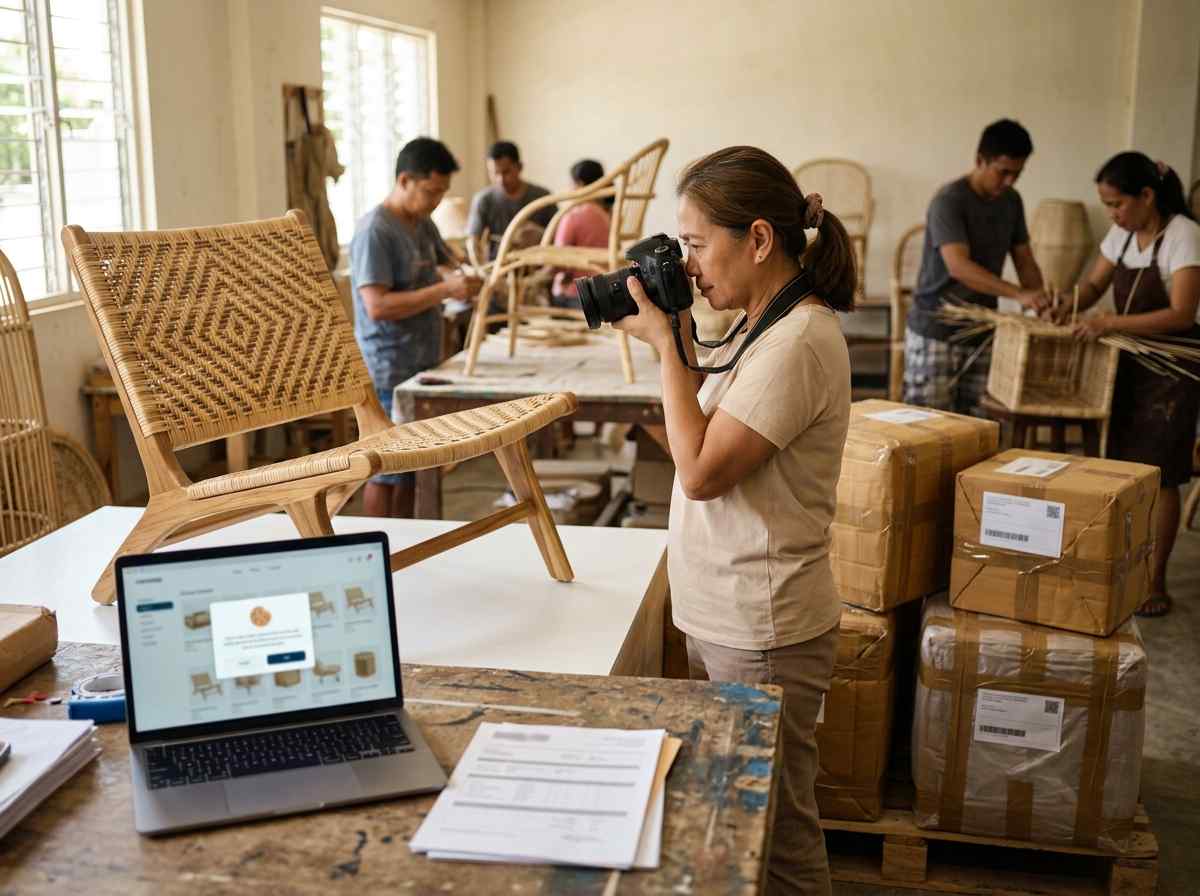
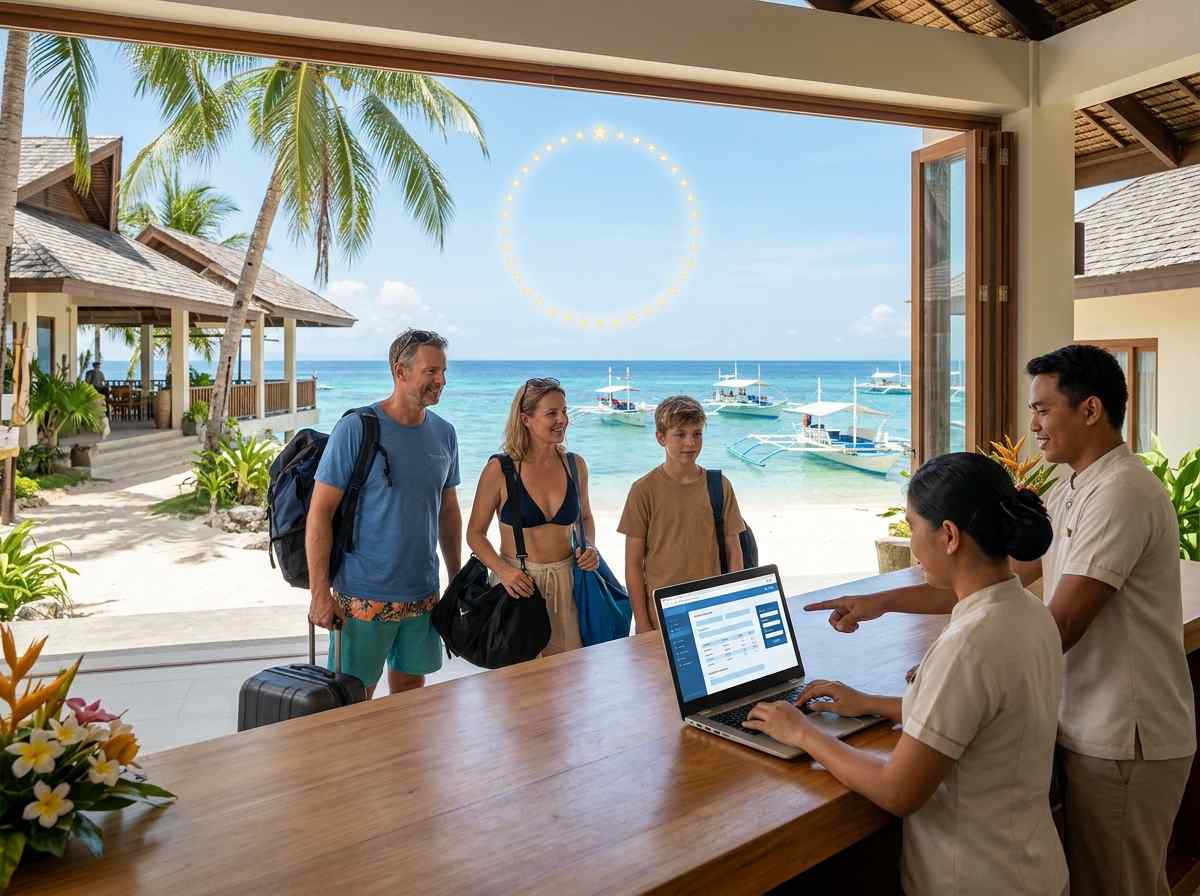
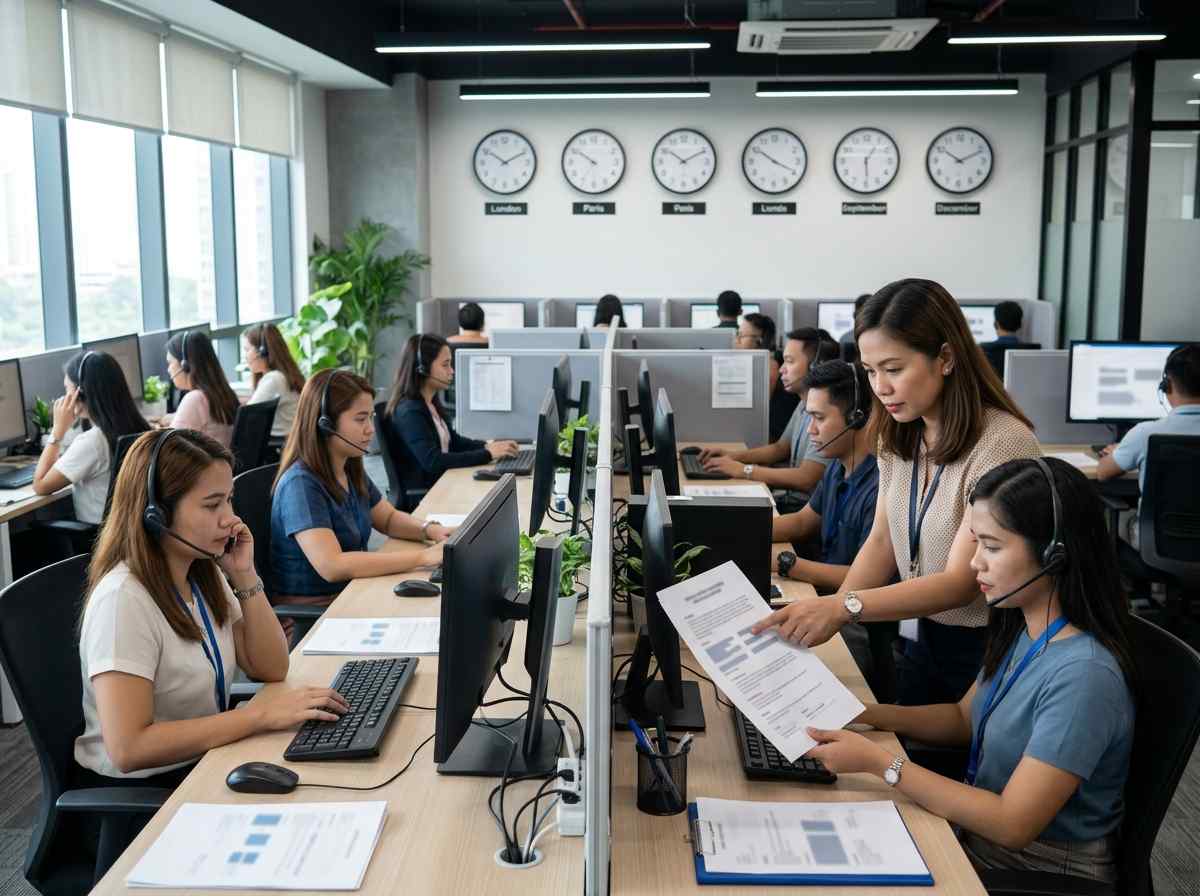
A German client sends a data processing agreement to a Lahug contact center. A Mactan dive resort launches a French-language booking page. A Mandaue furniture exporter starts selling directly to shoppers in the Netherlands. In each case, Europe’s privacy law has just arrived in Cebu. GDPR certification in Cebu is how these organizations show European clients and customers that personal data is handled lawfully and securely.
Univate Global helps Cebu organizations build a working GDPR compliance program and prepare for independent review. We map the personal data you handle, confirm your legal footing, close the gaps and assemble the evidence. Where a client or partner wants a formal credential, we also prepare you for an ISO/IEC 27701 or Article 42 certification audit.
Our consultants start from the way your business actually touches EU personal data. A BPO acting on a client’s instructions carries different duties from a resort that collects guest passports. An exporter running its own web store sits somewhere in between. We shape the program around your real role, so the effort goes where the legal risk sits.
Free ConsultationContact Us
Our Clients
GDPR Certification in Cebu for BPOs, Resorts and Exporters
The GDPR is a European law, but its reach is defined by whose data you handle, not where your office sits. Many businesses across Metro Cebu fall inside it without ever opening a European branch. Four groups raise the question with us most often.
IT-BPM operators and software firms come first. A Cebu IT Park delivery center may handle customer service, claims or back-office work for European brands. A software studio may host a European client’s user database. In both cases, the European client is the controller and the Cebu firm is its processor. The client will expect an Article 28 data processing agreement and proof that its data is protected.
Tourism and hospitality businesses form the second group. Beach resorts on Mactan Island, island-hopping tour operators and dive centers often market directly to European travelers. A booking site in German or Italian, prices in euros or advertising aimed at EU audiences can bring those guest records under the GDPR. Passport scans, dietary notes and dive medical forms make the data more sensitive still.
E-commerce sellers and exporters are the third group. Mandaue furniture and handicraft makers, Mactan electronics suppliers and dried mango exporters increasingly sell online to European buyers. Once they target EU consumers or track their behavior with analytics and advertising tools, the regulation can apply directly.
Universities and colleges complete the list. Cebu schools enroll European exchange students, run joint programs with European institutions and take part in research partnerships. Student files, application records and shared research data all need a clear legal basis and safe transfer arrangements.
How GDPR Certification Works in Cebu
The General Data Protection Regulation, formally Regulation (EU) 2016/679, has applied since 25 May 2018. It sets the rules for collecting, using, storing and sharing personal data about people in the European Union. Under Article 3(2), it also reaches organizations outside the EU that offer goods or services to people there or monitor their behavior.
It helps to be clear about the word “certification.” There is no single mandatory GDPR certificate that every organization must hold. Article 42 does allow approved certification mechanisms. Europrivacy, for example, was approved by the European Data Protection Board as a European Data Protection Seal in 2022. Most organizations, however, demonstrate compliance through a documented program, an independent assessment and often ISO/IEC 27701 certification.
In practice, our service has two parts. First, we help you build a GDPR compliance program that fits your role as controller, processor or both. Second, we prepare you for an independent assessment of that program. If you want a formal credential, the assessment can be an Article 42 certification or an ISO 27701 audit by an accredited certification body.
The roles stay separate. Univate is a consultant and does not issue Article 42 certificates or ISO certificates. An independent assessor or accredited certification body carries out the review. That separation is exactly what gives the result its weight with European clients.
Why Cebu Businesses Invest in GDPR Certification
For most Cebu companies, the trigger is commercial. European clients cannot legally hand personal data to a supplier that lacks adequate safeguards. Their procurement teams send privacy questionnaires, ask for records of processing and request breach procedures before signing. A prepared vendor answers these quickly. An unprepared one stalls the deal or loses it.
The legal exposure is real as well. Serious breaches of the regulation can draw fines of up to €20 million or 4% of worldwide annual turnover, whichever is higher. Non-EU controllers that fall under Article 3(2) usually need an EU representative under Article 27. European regulators have also become more active on cross-border cases, including those involving suppliers outside Europe.
The Philippines does not have an EU adequacy decision. That means every transfer of personal data from Europe to Cebu needs a recognized safeguard. For most businesses, that safeguard is the 2021 Standard Contractual Clauses, backed by a transfer risk assessment. European clients will check that you can honor what those clauses promise.
GDPR and the Philippine Data Privacy Act
Cebu organizations already work under the Data Privacy Act of 2012 (Republic Act 10173), enforced by the National Privacy Commission. The two laws overlap in useful ways. Both expect a data protection officer, appropriate security measures and prompt breach reporting. NPC Circular 16-03 sets a 72-hour window for notifying the Commission, much like the GDPR’s Article 33. The differences matter too. The GDPR reaches across borders, structures lawful bases differently and adds strict EU transfer rules. A good program builds on your existing Data Privacy Act work rather than duplicating it.
GDPR Requirements: What Your Organization Will Need
The regulation describes outcomes rather than a fixed checklist. A ten-person dive operator and a 3,000-seat BPO will meet it in very different ways. Still, any assessor or European client will look for evidence of the same core obligations:
- A lawful basis for each processing activity, such as contract, consent, legal obligation or legitimate interests
- Clear privacy notices that tell people what you collect, why, how long you keep it and who receives it
- Processes to handle data subject rights, including access, correction, erasure, objection and portability
- Records of processing activities under Article 30, kept up to date as your services change
- Data protection by design and by default under Article 25, built into systems and projects
- Security of processing under Article 32, with controls matched to the risk to individuals
- Breach detection and notification to the supervisory authority within 72 hours under Article 33
- Data protection impact assessments under Article 35 for high-risk processing
- A data protection officer where Article 37 requires one, plus processor contracts and transfer safeguards
Paperwork is only half the picture. An assessor will ask your team how a deletion request is handled, sample breach logs and test whether retention rules are applied. That is why we spend as much time on daily practice as on drafting documents.
Ownership matters too. Projects move faster when a senior sponsor is named and a small working group from operations, IT, HR and legal owns the tasks. In many Cebu companies, the existing Data Privacy Act DPO is the natural lead.
Our Process for GDPR Certification in Cebu
Our approach to GDPR certification in Cebu runs in six stages. Each stage produces something you can show a client, and each one sets up the next. You always know what has been done and what your team needs to supply.
Step 1 – Data Mapping and Gap Analysis
We start by finding out what EU personal data you hold and where it travels. Workshops with each team trace data from collection through storage, sharing and deletion. We then compare your current practice against the regulation and your Data Privacy Act program. The result is a data inventory, a draft record of processing and a prioritized gap report.
Step 2 – Lawful Basis, Transfers and Risk
Next, we confirm the legal footing for each activity. We document the lawful basis, settle whether you act as controller or processor, and review how data reaches Cebu from Europe. Where processing is high-risk, such as large-scale monitoring or health data, we run data protection impact assessments with your team. We also check whether you need an EU representative or a DPO.
Step 3 – Policies, Notices, Contracts and Controls
We then draft and adapt what the program needs. That includes privacy notices, a rights-handling procedure, retention rules and a breach response plan. On the contract side, we review data processing agreements and Standard Contractual Clauses with your clients and subprocessors. Security and privacy controls are put in place within the tools you already use, and staff receive role-based awareness training.
Step 4 – Internal Audit and Management Review
Before any outside review, we audit the program ourselves. We test a sample of processing activities, rights requests, vendor contracts and security controls. Findings are tracked to closure. Your leadership then holds a management review to confirm resources, accept residual risks and approve the program.
Step 5 – Independent Assessment or Certification Audit
Now the program faces an independent reviewer. For many Cebu firms, that is an independent GDPR compliance assessment that European clients can rely on. Others choose a formal route, such as an Article 42 scheme like Europrivacy or an ISO 27701 audit by an accredited certification body. We prepare your team, organize the evidence and help you respond to any findings.
Step 6 – Ongoing Monitoring
Privacy compliance is never finished. New clients, new tools and new markets change your data flows. We can support periodic reviews, DPIA updates, refresher training and breach drills. We also track regulatory change, such as the EU’s Digital Omnibus proposal, so your program adjusts if the rules move.
Typical GDPR Timeline for Cebu Organizations
The table below shows indicative durations for a small or mid-sized organization with one main site. Your actual timeline depends on the number of processing activities, your role and how mature your Data Privacy Act program already is.
| Phase | Key activities | Indicative duration | Main output |
|---|---|---|---|
| Data mapping and gap analysis | Team workshops, data flow tracing, review against GDPR and Data Privacy Act | 2–3 weeks | Data inventory, draft Article 30 records, gap report |
| Lawful basis, transfers and risk | Lawful basis decisions, controller or processor analysis, transfer review, DPIAs | 2–4 weeks | Lawful basis register, transfer assessment, DPIA reports |
| Policies, contracts and controls | Notices, rights procedure, retention rules, DPAs and SCCs, security controls, training | 6–10 weeks | Working privacy program with records |
| Internal audit and review | Sample testing, corrective actions, management review | 2–3 weeks | Internal audit report and closed findings |
| Independent assessment or certification | Independent GDPR assessment, Article 42 audit or ISO 27701 audit | 2–8 weeks, including scheduling | Assessment report or certificate from the independent body |
Most single-site organizations complete the program and the independent review in four to seven months. Firms pursuing ISO 27701 without an existing ISO 27001 system, or those with many EU clients and subprocessors, should plan for longer.
GDPR Certification in Cebu: Cost and Timeline
No honest consultant can price a GDPR project before seeing your data flows. The work depends far more on what you do with personal data than on how many people you employ. These factors shape the cost of GDPR certification in Cebu.
Processing Activities and EU Data Volume
Each distinct processing activity needs a lawful basis, a record and a retention rule. A resort with a booking engine and a guest list has a short register. A BPO serving twelve European clients across several campaigns has a long one. Large volumes of EU records, or any special category data such as health details, also raise the depth of risk work.
Controller or Processor Role
Controllers decide why and how data is used, so they carry the full set of duties, including notices and rights handling. Processors act on a client’s instructions and focus on Article 28 terms, security and subprocessor control. Many Cebu firms are both: a processor for clients and a controller for their own staff and marketing data.
International Transfers
Data moving between Europe, Cebu and any third countries needs safeguards on every leg. The more clients, subprocessors and cloud regions involved, the more Standard Contractual Clauses and transfer assessments must be reviewed. Onward transfers to vendors in other countries add further work.
Existing Data Privacy Act Program and Certification Route
An organization with a registered DPO, current privacy manual and tested breach procedures under the Data Privacy Act starts well ahead. The route you choose also matters. An independent compliance assessment is the lighter path. An Article 42 certification or ISO 27701 audit adds audit fees and formal requirements, and ISO 27701 builds on an ISO 27001 system.
If you choose a certification route, use an accredited body. For ISO 27701, that means a certification body accredited by the Philippine Accreditation Bureau or another IAF member. For Article 42 schemes, it means a body accredited for that scheme. Consulting and audit fees are always separate. Once we see your scope, we send a clear, itemized quote.
On timing, most Cebu organizations with one main site reach the independent review in four to seven months. The biggest factor is usually internal: how quickly your teams complete data mapping and sign off documents. For organizations with sites in several cities, see our page on GDPR certification in the Philippines.
Benefits of GDPR Certification for Cebu Businesses
A well-run program does more than avoid fines. Organizations that complete GDPR certification in Cebu usually notice commercial and operational gains within the first year.
Faster European Deals
European procurement teams ask the same privacy questions every time. With records, contracts and an independent assessment ready, your team can answer in days rather than weeks. That helps Cebu suppliers compete for European work against vendors in Manila, India and Eastern Europe.
More Trust From European Travelers and Buyers
Guests and online shoppers increasingly read privacy notices and cookie banners. Clear notices and respectful marketing practices signal a professional operation. For a Mactan resort or a Mandaue web store, that trust can turn into bookings and repeat orders.
Cleaner, Leaner Data
Data mapping often uncovers old spreadsheets, forgotten backups and records kept long past their purpose. Deleting what you no longer need cuts storage costs and shrinks the damage of any future breach. It also makes rights requests far easier to handle.
Better Breach Readiness
Typhoons, power failures and cyberattacks all test a company’s response. A tested breach plan sets out who assesses an incident and who informs the client. It also shows how the 72-hour deadlines under the GDPR and NPC Circular 16-03 are met. That calm, coordinated response protects client relationships.
A Platform for Other Standards
GDPR work overlaps heavily with ISO 27701 privacy management. It also builds on the security system behind ISO 27001 certification in the Philippines. Controls, records and audits can be shared across them. Building once and reusing evidence saves time as client demands grow.
Why Cebu Companies Choose Univate for GDPR
Univate has consulted more than 300 enterprises on cybersecurity and compliance. Our team has delivered over 500 executive sessions on cybersecurity, AI governance and data privacy. Our consultants include CISA-certified professionals and specialists with decades of experience in security, risk and governance. From our Philippine office in Makati, we understand both the Data Privacy Act and what European clients expect from their suppliers.
We write programs your people can run. Notices match your real booking flows, rights procedures fit your helpdesk, and contracts reflect how data actually moves. We stay on the consultant side of the line. We prepare you, and an independent assessor or certification body reviews you. That keeps the outcome credible and our advice impartial.
Many Cebu firms face several frameworks at once. We design your privacy controls to support ISO 27001 certification in Cebu and SOC 2 as well, so evidence is gathered once and reused. That joined-up approach makes GDPR certification in Cebu part of a wider assurance plan rather than a separate project.
GDPR Certification Services Across Cebu
We deliver GDPR certification in Cebu through a hybrid model. Data mapping workshops, document reviews and progress calls run remotely. On-site visits are planned for key milestones, such as initial interviews, the internal audit and assessment preparation.
In Cebu City, we work with BPOs and software firms in Cebu IT Park in Lahug and Cebu Business Park. We also support service companies in the South Road Properties. In Mandaue, we support furniture and handicraft exporters, distributors and IT providers along A.S. Fortuna and the North Reclamation Area. On Mactan Island, we support resorts, dive operators and travel businesses in Lapu-Lapu, as well as export manufacturers in the Mactan Economic Zone.
We also work with organizations in Talisay, Consolacion, Liloan and Minglanilla. Further afield, we support Bohol and Negros Oriental, where resorts and dive centers also welcome European guests. Teams with offices in the capital can pair this work with our GDPR certification in Manila service. For other locations, see our ISO certification in the Philippines hub.
Planning GDPR certification in Cebu?
Tell us about your scope, your sites and your timeline, and we will come back with a clear plan.
Client Testimonials
It was really a great partnership with their team.
Sultan
I had the pleasure and opportunity of working with Univate Solutions on a couple of High Maturity (ML5) CMMI appraisals and found them to be one of the best.
Amulya P
Team Univate holds many professional approaches.
Ashish Sherlekar
GDPR Certification in Cebu: Frequently Asked Questions
Does GDPR certification in Cebu apply if we have no office in Europe?
Yes, it can. The GDPR applies to organizations outside the EU that offer goods or services to people in the EU or monitor their behavior. It also reaches Cebu processors through the contracts they sign with European clients.
Is there an official GDPR certificate?
There is no single mandatory certificate. Article 42 allows approved certification schemes, such as Europrivacy. Most organizations instead rely on a documented compliance program, an independent assessment and, often, ISO 27701 certification.
Our BPO only follows client instructions. What do we need?
As a processor, you need an Article 28 data processing agreement with each client, along with suitable security measures. You must also control your subprocessors, help clients answer rights requests and report breaches to the client without undue delay.
Does a Mactan resort need to comply with the GDPR?
It depends on how you market. A resort that actively targets European guests, for example with EU-language pages, euro pricing or EU-focused advertising, is likely in scope. A resort whose website is simply reachable from Europe may not be.
We already comply with the Data Privacy Act. Is that enough?
It gives you a strong head start, but it is not the same law. The GDPR adds its own lawful-basis rules, extraterritorial reach and strict conditions on transfers from Europe. A gap analysis shows exactly what to add.
Do we need an EU representative?
Non-EU controllers or processors caught by Article 3(2) usually must appoint one under Article 27. Limited exceptions exist for occasional, low-risk processing. We help you assess whether you qualify for the exception.
How are transfers from Europe to the Philippines handled?
Because the Philippines has no EU adequacy decision, transfers need a safeguard. Most businesses use the 2021 Standard Contractual Clauses, supported by a transfer risk assessment and matching security measures.
How does ISO 27701 relate to the GDPR?
ISO 27701 extends an ISO 27001 security system into privacy management. Accredited bodies certify it, and its controls map closely to GDPR duties. Many European clients accept it as strong evidence of compliance.
Will the GDPR change soon?
The EU’s Digital Omnibus proposal, published in November 2025, would amend parts of the GDPR. It is still in the legislative process. We monitor it and will update your program if final changes affect you.
Start Your GDPR Certification Project in Cebu
Perhaps a European client has sent a privacy questionnaire, or you plan to market to EU travelers next season. Either way, the first step is a short conversation about your data, your clients and your deadlines. Our consultants will review where you stand and recommend the right route for GDPR certification in Cebu, with a clear, itemized proposal.
Book a Free Consultation Call +63 963 451 6528Prefer to talk first? Call our Philippines team on +63 963 451 6528, or send us your requirements through the contact form.
Email: info@univateglobal.com






